About
January 1, 0001
ROOTCON
ROOTCON is the Philippines’ premier and largest hacking conference, founded in 2008 by Dax Labrador, better known in the community as Semprix. What started as a grassroots gathering of hackers and security enthusiasts has grown into a internationally recognized platform for knowledge sharing, responsible disclosure, and community-driven innovation. ROOTCON continues to uphold its mission of bringing together cybersecurity professionals, developers, students, and researchers under one roof to explore and challenge the ever-evolving digital frontier.
As the cornerstone of the Philippine hacking community, ROOTCON has built a reputation for its deeply technical content, inclusive atmosphere, and uniquely hacker-centric traditions. From live demos of real-world exploits to Capture the Flag competitions, badge hacking, and the ever-infamous Hacker Jeopardy, ROOTCON fosters an environment where curiosity thrives and collaboration is key. It proudly represents the spirit and talent of Filipino hackers — relentless in exploration, rich in knowledge, and driven by purpose.
ROOTCON has become more than just a conference — it’s a movement that empowers ethical hacking, mentorship, and community growth across the country. Whether you’re a red teamer, blue teamer, or just taking your first steps into cybersecurity, ROOTCON offers a space to connect, learn, and be inspired. As the Philippine infosec landscape continues to grow, ROOTCON stands as a guiding force for those who believe in hacking with purpose, driven by integrity and a passion for positive impact.
Founder's Note:
ROOTCON was born out of a simple idea — to create a safe space for Filipino hackers to connect, learn, and grow. Back in 2008, there were no local platforms that embraced the hacker mindset the way we do today. I wanted to build something raw, real, and rooted in community — and that’s how ROOTCON began.
-Semprix
Black Badge
January 1, 0001
What is a Black Badge
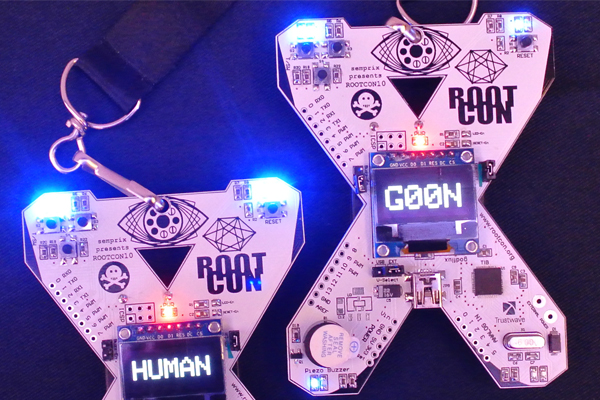
Black Badge has been adopted from DEF CON, a black badge is one of the highest honors given to the ROOTCON con-goers who proved their elite skills, black badge are also given to people who have significant contributions to the local InfoSec community.
How to acquire one?1. Join the official ROOTCON contests.
2. Make significant contribution to the local InfoSec community.
1. Free single pass to the next ROOTCON event.
2. Community bragging rights.
3. Your name / team name will be put up on the ROOTCON Hall Of Fame.
Black Card
January 1, 0001
UPDATES
Updated: Sat May 30 20:28:20 PST 2026
Revisions: c8080f83de1431ed94db428ef1197edd7cf28b2f
As ROOTCON marks its 20th year, we’re opening a new chapter for one of the community’s most recognized distinctions.
The ROOTCON Black Card — long known as a symbol of trust, contribution, and commitment — is once again open to the public for 2026.
This special anniversary year is about coming home to the community that built ROOTCON. Reopening Black Card access gives more members the opportunity to be part of an elevated experience during this milestone celebration.
Opening registration does not change what the Black Card represents. Holders are still expected to embody the spirit of the community — professionalism, respect, and a genuine passion for sharing knowledge and strengthening the security scene.
ROOTCON 20 is about legacy, community, and the people who make this space what it is. The Black Card remains a mark of that connection — now reintroduced for a new generation.
Sign up for the ROOTCON Black Card and unlock exclusive perks and VIP experiences at ROOTCON 20 — open to the public for this year only.
https://rootc.onl/blackcardreg
CFP Review Board
January 1, 0001
 Semprix "The Fork Meister" His two decades of hacking experience allowed him to serve multiple Fortune 100 companies with specialized knowledge in offensive security and defense against attacks on infrastructure while applying hacker mindset approaches to problem-solving.
Semprix manages ROOTCON chaos by expertly balancing speakers and unexpected emergencies while maintaining style and caffeine support. His reputation stems from his ability to curate impactful talks and build durable communities while maintaining the underground vibe in today's corporate-dominated environment.
Code of Conduct
January 1, 0001
Readme
ROOTCON is committed to providing a safe, inclusive, and respectful environment for all participants, including attendees, speakers, sponsors, staff, and volunteers. The following Code of Conduct outlines the expected behavior and guidelines to ensure everyone enjoys a positive and welcoming experience.
1. Respect for All
ROOTCON embraces diversity and inclusion. We welcome participants from all backgrounds and are committed to creating an environment free from discrimination and harassment. Any form of disrespectful, abusive, or inappropriate behavior will not be tolerated. This includes, but is not limited to:
• Offensive comments or behavior related to gender, sexual orientation, gender identity, disability, race, ethnicity, age, religion, or physical appearance.
• Unwelcome sexual attention or advances.
• Harassment, stalking, or deliberate intimidation.
• Disruptive behavior during talks, workshops, or any conference activity.
• No individual is entitled to special treatment, favors, or exceptions based on sexual orientation or any other personal attribute.
2. Consent and Boundaries
• Photography & Recordings: Always ask for permission before taking photos or videos of other attendees. Respect requests not to be photographed or recorded.
• Personal Space: Be mindful of personal boundaries. Respect the space and privacy of fellow attendees, including their property.
• Physical Contact: Any form of unwelcome physical contact is strictly prohibited.
3. Healthy Debate & Civil Discourse
ROOTCON encourages discussion, debate, and learning, but always in a respectful manner. We ask that you:
• Allow others to share their thoughts without interruption.
• Disagree respectfully and avoid personal attacks or inflammatory remarks.
• Be open to learning from others, including those with different perspectives.
4. Alcohol & Substance Use
ROOTCON may host events where alcohol is served (e.g., Beer Bash). We ask that attendees drink responsibly and be respectful of others. Excessive intoxication, disruptive behavior, or the use of illegal substances will not be tolerated and may result in removal from the event.
5. No Disruptive Behavior
Disruptive actions, such as heckling during talks or breaking the flow of workshops, are not allowed. Respect the speaker and fellow participants by keeping noise levels down and participating in an orderly manner.
6. No Weapons or Illegal Activity
Weapons of any kind (including concealed firearms, knives, or other dangerous objects) are strictly prohibited at ROOTCON. Any illegal activities, including hacking outside the bounds of event-sanctioned challenges or violating local laws, will result in immediate ejection from the event and involvement of local authorities if necessary.
7. Ethical Hacking Only
While ROOTCON celebrates hacking culture, all hacking activities should be confined to approved, event-sanctioned challenges and environments. Unauthorized access to other attendees' devices or any form of malicious hacking is strictly prohibited.
8. Follow Staff Instructions
ROOTCON staff and volunteers are here to ensure the event runs smoothly. Please follow any instructions or guidance provided by event staff, especially in the case of safety or emergency procedures.
9. Reporting Violations
If you experience or witness behavior that violates this Code of Conduct, we encourage you to report it immediately to a ROOTCON staff member or volunteer. Reports can be made in person or anonymously.
• Anonymous Reporting Form: https://rootc.onl/incidentreport
• via Signal:
@Eman0n
All reports will be handled with confidentiality and respect.
10. Consequences of Violations
ROOTCON reserves the right to take any necessary actions to enforce this Code of Conduct, including:
• Verbal warnings.
• Immediate removal from the event without a refund.
• Involvement of local authorities for severe offenses.
Updated: Sat May 30 20:28:20 PST 2026
Revisions: d62d6839f26aa8fb5480d71e9304de8b7b1f483f
Community
January 1, 0001
Safe Harbor Initiative
Our very own Semprix, together with the Philippine hacking community and the Department of Information and Communications Technology (DICT),
is working together on the development of the country’s first comprehensive Safe Harbor and Responsible Disclosure Policy Guidelines.
This landmark collaboration aims to formalize the relationship between ethical hackers, private organizations, and the government — promoting a safer,
more transparent, and more collaborative cybersecurity ecosystem across the Philippines.
For years, local security researchers have operated in a gray area —
eager to report vulnerabilities that could compromise systems, but often held back by the fear of legal repercussions or misunderstanding.
The proposed Safe Harbor framework seeks to address this long-standing gap by providing legal protection and clear boundaries for researchers acting in good faith.
Under the forthcoming policy, those who responsibly disclose vulnerabilities following defined procedures will be shielded from prosecution, provided their actions align with ethical and non-destructive intent.
At the same time, the Responsible Disclosure component of the policy will guide organizations — both in the public and private sectors —
on how to receive, evaluate, and respond to vulnerability reports. It will establish best practices for communication, validation, and remediation,
ensuring that vulnerabilities are addressed promptly while maintaining trust and confidentiality between researchers and system owners.
This dual framework aims to foster a culture of accountability, openness, and mutual respect between the security community and the institutions they help protect.
This initiative also underscores the growing recognition of ethical hackers as key partners in national cybersecurity resilience.
By collaborating with DICT, Semprix and the hacking community are paving the way for structured engagement between independent researchers and government agencies —
echoing global models such as the U.S. Department of Justice’s vulnerability disclosure guidelines and the EU’s coordinated disclosure frameworks.
Once finalized, the Safe Harbor and Responsible Disclosure Guidelines will serve as a cornerstone for the Philippines’ cybersecurity maturity roadmap, encouraging more organizations to adopt responsible vulnerability disclosure programs and recognize the vital role of ethical hackers. Through this effort, the hacking community and DICT are not only strengthening defenses but also redefining the narrative — that hackers, when guided and protected by the right policies, can be powerful allies in securing the nation’s digital future.
Conference Archives
January 1, 0001
Missed the CON?
Get hold of the past ROOTCON events. All materials here posted are with its proper permission from the speaker and presentor and is copyrighted by ROOTCON.
ROOTCON 19
(Augmented Threats)
September 24, 25 & 26, 2025
Royce Hotel & Casino, Clark, Pampanga
» Archives
ROOTCON 18
(Interconnected Realities)
September 25, 26, 27, 2024
Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 17
(Surveillance, Technology and Privacy)
September 27, 28, 29, 2023
Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 16
(Hard Wire)
September 28, 29, 30, 2022
Hybrid - Zoom Webinar, Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 15
(Rebooted)
October 12-15, 2021
Zoom Webinar, Discord
» Archives
(Recovery Mode)
October 7-10, 2020
Zoom Webinar, Discord, Twitch
» Archives
ROOTCON 13
(Theme: Two Faces of Tomorrow)
September 25-27, 2019
Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 12
(Theme: Hackers: Heroes of Computer Revolution)
September 27-28, 2018
Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 11
(Theme: Humans meets IoT)
September 21-22, 2017
Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 10
(Theme: Digital Heist)
September 22-23, 2016
Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 9
(Theme: Hacker Dystopia)
September 18-19, 2015
Taal Vista Hotel, Tagaytay City
» Archives
ROOTCON 8
(Theme: Hack Eight)
September 26-27, 2014
Parklane Hotel, Cebu City
» Archives
ROOTCON 7
(Theme: Pirates V.S. Ninjas)
September 13-14, 2013
Parklane Hotel, Cebu City
» Archives
ROOTCON 6
(Theme: Cyber Espionage)
September 7-8, 2012
Parklane Hotel, Cebu City
» Archives
ROOTCON 5
(Theme: Digital Biohazard)
September 9-10, 2011
Parklane Hotel, Cebu City
» Archives
ROOTCON 4
(Theme: ROOTCON Genesis)
October 23, 2010
Congo Grill, Ortigas, Pasig City
» Archives
ROOTCON 3
(Theme: Pinoy Hackers)
December 12, 2009
BayView Hotel, Manila City
» Archives
ROOTCON 2
(Theme: Beers & Pongs)
April 04, 2009
TOSH, Makati City
» Archives
ROOTCON 1
(Theme: The Inception)
December 20, 2008
Handuraw Pizza, Cebu City
» Archives
Contact Us
January 1, 0001
Get in touch
General Info
General inquiries, comments and suggestions.
info /at/ rootcon /dot/ org.
Marketing & Sponsors
Marketing and Sponsorship related inquiries contact
sponsors /at/ rootcon /dot/ org.
Methadone
The omnipotent being at ROOTCON
methadone /at/ rootcon /dot/ org.
Data Retention
January 1, 0001
Readme
1. Purpose
This Data Retention Policy outlines the practices for collecting, storing, managing, and securely disposing of data gathered by ROOTCON. The goal is to ensure data is retained only as long as necessary to fulfill the purposes for which it was collected, in compliance with applicable data protection regulations.
2. Scope
This policy applies to all personal, event-related, and operational data collected by ROOTCON, including but not limited to:
• Attendee registration information
• Sponsorship agreements and details
• Speaker and vendor details
• Transactional data related to ticket sales or merchandise
3. Data Retention Periods
Data retention periods vary depending on the type of data. The following retention guidelines apply unless legal obligations or operational needs require different timeframes:
• Attendee Information: Retained for a maximum of 3 years from the date of the event for communication and future marketing purposes, unless opted out by the attendee.
• Sponsorship Data: Retained for 5 years to maintain historical partnership records, compliance, and accounting purposes.
• Speaker and Vendor Information: Retained for 5 years for event coordination, historical records, and future partnerships.
4. Data Deletion
After the retention period, all personal data will be securely deleted or anonymized to protect the privacy of individuals and meet regulatory requirements. This includes:
• Deleting digital records from databases and cloud systems.
• Securely destroying physical records.
• Anonymizing data that may be useful for statistical purposes without retaining personally identifiable information (PII).
5. Data Access and Security
Data will only be accessible to authorized personnel involved in organizing ROOTCON, under strict data security measures, including:
• Encryption of sensitive data.
• Access control mechanisms to prevent unauthorized access.
6. Policy Updates
This policy will be reviewed annually or whenever necessary to reflect changes in operational or regulatory requirements.
By implementing this policy, ROOTCON ensures compliance with data protection standards while respecting the privacy of its attendees, sponsors, and contributors.
Updated: Sat Sep 21 08:33:22 PST 2024 revision: 990a8006133018cf2086c5e8a3daea9e91da4a15
Events
January 1, 0001
ROOTCON 20 is a big one for us. Twenty years doesn’t happen every day, and we didn’t want to celebrate it with just a bigger stage and louder speakers.
So aside from the main conference, we’re putting together a series of events throughout the year where the community can actually spend time together. Smaller meetups, sports activities and random side events. The kind of gatherings where you can talk properly, laugh a bit, and get to know people beyond their badges and handles.
Some of the best parts of ROOTCON have always happened outside the talks anyway.
This year, we’re just making more space for that.
FAQ
January 1, 0001
What is ROOTCON?
ROOTCON is the premier and largest hacking conference in the Philippines.
Where did the name ROOTCON came from?
ROOTCON came from the two words root (a super-user) and con (conference).
When is ROOTCON?
ROOTCON is held within the month of September and October.
What is a badge?
A badge is your ticket to the CON. ROOTCON have 2 types of badge an electronic badge and non-electronic badge.
What is a black badge?
A black badge is an honor given to players who won the ROOTCON official contests, it will give you a free pass on the next conference.
What is an electi badge?
An electi badge is a badge given to night track speakers, where it will hold a perpertual free access to ROOTCON.
What is a goon? and how to be one?
Goons are people who dedicated theirselves to help run the conference, and make it as a special one. To be a goon you need to be endorsed by a fellow goon, you will then start being an apprentice goon
before getting endorsed to become an official one.
How to register to the conference, and how do I pay?
Since ROOTCON 6 we use EventBrite as our third-party payment gateway, where you can pay through direct bank deposit or PayPal.
I'm a speaker. Do I have to pay?
ROOTCON does not earn something, speakers are not paid in monetary form, they are only given tokens and other appreciation materials,
speakers dont need to pay, as a speaker you will get your speakers badge, booze and food for free.
I'm low on budget, how do I go to ROOTCON?
We are making ROOTCON the most affordable but the best quality of conference, if you are low on budget and still want to attend ROOTCON, you may have several options.
1. ROOTCON event dates will be announced ahead of time, grab yourself a coin box and put some coins on it before the CON
2. Meet and make you new friends ask someone if you can crash at their hotel rooms.
3. Ride sharing, ask someone at the Facebook ROOTCON Discussions group if you can ride with them going to the venue.
Is ROOTCON only for hackers?
No, ROOTCON is open to everyone, being a hacker does not choose any profession.
I'm a minor, can I attend?
Minors should be accompanied by parents or guardians, there will be activities during the CON that requires parental guidance, events like beer drinking contest, wargames, and other adult stuffs.
I'm a corporate IT security professional, should I attend ROOTCON?
We suggest you do attend the CON, Information Security is a fast phase industry, ROOTCON can help you catch up with the latest trend in Information Security.
You will also expand your social network within the industry.
What do I bring during the CON?
It depends on what do you want to bring and what you plan to do on during the conference.
What behaviors that are acceptable on ROOTCON?
Don't be a douchebag and a show whore.
Will there be illegal activities on the CON?
No, we do not condone illegal activities during the CON.
Is this event legitimate?
Yes this event is legitimate, we abide by the laws and rules.
Do you give official receipt?
Yes we provide official receipts but only by request, read the event page for details and instructions.
Do you issue Certificates after the con?
ROOTCON is a hacker conference and not a seminar, training or a workshop so we do not "normally" issue certificate.
However if it makes you happy we can provide an official certificate of attendance digitally signed by semprix (The Fork Meister).
Do you provide copy of presentations?
There will be no hard-copy that will be given during the event, you may approach the speaker if you cannot wait for the event archives to go live.
There will be a local mirror of the ROOTCON media server at the conference, you may download the event archives from 1 to the current at high-speed.
Are you connected with any government Feds or agency?
NO!!! We are not connected in any government feds or agency.
Do you hack Facebook, Twitter, Yahoo mail and get paid?
NO!!! We dont hack your Facebook, Twitter or Yahoo mail, we dont hack your girlfriends/boyfriends email account for you.
You guys are involved in hacking Philippine government website?
NO!!! We are not a group of underground hackers attempting to bring down IT infrastructure in the Philippines.
Where do I ask my question, this FAQ is not helpful at all
If your question is not anwered by this FAQ, send an email to info /at/ rootcon dot org.
Updated: Sat May 30 20:28:20 PST 2026
Revisions: 5e2b33ab1d9bf620cbbf853ac81fb328e91c08ae
Goons
January 1, 0001
Meet the Goons
ROOTCON is made up of many people, all who has different Kung-Fu skills, each year they gather to setup and launch the premier hacking conference in the Philippines, to gather hackers, geeks, and pros to practice and show off their skills in alcoholic drinking, debugging, packet sniffing, and socializing. It's due to their hardwork and commitment that made it happen, without these people ROOTCON won't be a reality.
Hack Sauce
January 1, 0001
Fuel Your Hacks with Fire!
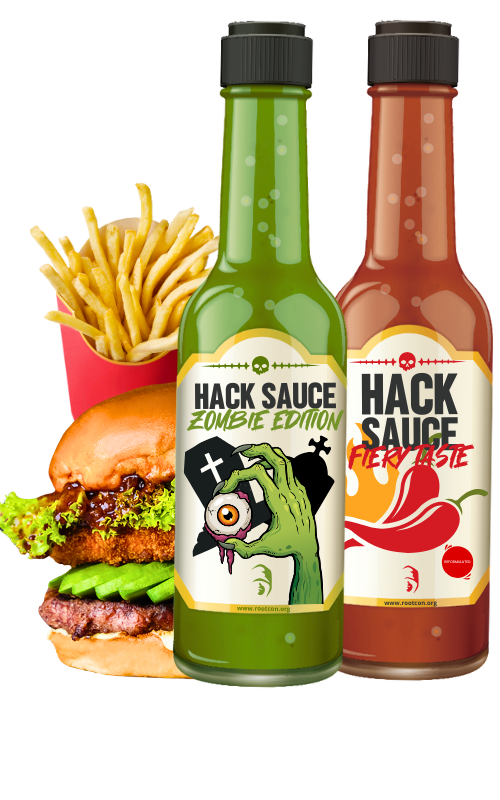
Introducing ROOTCON Hack Sauce — the only hot sauce with enough heat to match your hacking skills. Whether you’re crushing code, dominating CTFs, or simply looking to level up your snack game, this sauce is crafted to ignite your taste buds and spark your creativity.
Hack Your Taste BudsFrom late-night coding sessions to quick bites on the con floor, ROOTCON Hack Sauce is your perfect companion. Drizzle it on burgers, tacos, pizza, burritos, or—if you’re truly fearless—take it straight by the spoon. Your call, hacker.
Hall Of Fame
January 1, 0001
Official Contests
Capture The Flag -- The most grueling game in every hacking conference, ROOTCON is no different! This game is not for the faint-hearted it requires sleepless nights of problem-solving, cryptos, puzzles, and exploitation. The game is played with maximum of 2 team members and maximum of 3.
Hacker Jeopardy -- Do you have a liver of a metal, up-to-date with the latest technologies, or have a geekish, nerdish historian-fu skills? This game is for you.
Mystery Challenge -- An immersive challenge that will test your deductive skills, critical thinking, and ability to unravel a cryptic puzzle shrouded in intrigue and of course your hack-fu skills. Prepare to step into the shoes of an amateur sleuth as you navigate through the enigmatic twists and turns of The Mystery Challenge.
WiFinder (War Driving) (NEW) — Channel your inner wardriver as you hunt for hidden wireless networks across the ROOTCON grounds. Armed with your laptop, GPS, and Wi-Fi adapters, you’ll track, map, and log access points in real-world conditions. It’s not just about finding signals — it’s about precision, stealth, and understanding the art of wireless reconnaissance.
Hacker Karaoke (NEW) — Drop the mic, raise the packet! Hacker Karaoke is where code meets chords and firewalls meet falsettos. Whether you’re belting out 80s classics or meme-worthy anthems, this event is all about having fun, letting loose, and proving that even hackers can hit those high notes (or at least try to).
Links
January 1, 0001
Security Sites
Offensive Security : Offensive Security is an Online Information Security Training and the guys behind Kali Linux
Social Engineering - Security Through Education: The Official Website of the Social Engineering Framework(Art Of Human Hacking).
Metasploit Unleashed By Offensive Security: The free online version of the course for Metasploit
THN (The Hacker News): The Hackers News is an online Hacker News Organisation that propagates news specifically related to information security threats, hacking threads and issues from all over the world.
SecLists.Org: Internet Security Resource Website that gives full disclosure.
SoldierX: No body can stop information dissemination.
SANS Internet Storm Center: SANS Internet Storm Center is a Cooperative Network Security Community
Schneier on Security: Bruce Schneier's Website about Information Security
Infocon: massive repository of all hacking conference content.
DEF CON: Official website of the world's largest hacking conference in the world.
Hackaday: The world's largest collaborative hardware slash the hardware hacking development community.
Toolswatch: Hacker's Arsenal Portal
News Feed
January 1, 0001
Old Time Hall Of Fame
January 1, 0001
Do you have what it takes?
Our conferences does not only hold cutting-edge talks, each year ROOTCON hosts mind-boggling contest that are participated by con-goers, aside from getting your team onto the Hall Of Fame, winners gets to take home a black-badge, which entitles the players for a FREE entrance the next con.
 Capture The Flag
ROOTCON 13 - [hsb]G3{God’s Gift to Girls}
ROOTCON 12 - Team Harambae
ROOTCON 11 - Ethical Hackers Club
ROOTCON 10 - Team Harambae
ROOTCON 9 - Team Handshake
ROOTCON 8 - Team Jill
ROOTCON 7 - Team Handshake
ROOTCON 6 - No Winner
ROOTCON 5 - No Winner
Policies
January 1, 0001
Privacy Policy
Updated: Sat May 30 20:28:20 PST 2026
Revisions: 8ea9d5d3f249899ec37b4b8c99a32c497e892f02
Terms & Condition
Updated: Sat May 30 20:28:20 PST 2026
Revisions: 8ea9d5d3f249899ec37b4b8c99a32c497e892f02
Code of Conduct
Updated: Sat May 30 20:28:20 PST 2026
Revisions: 8ea9d5d3f249899ec37b4b8c99a32c497e892f02
Safety Waiver
Updated: Sat May 30 20:28:20 PST 2026
Revisions: 8ea9d5d3f249899ec37b4b8c99a32c497e892f02
Press
January 1, 0001
Media Coverage
ABS-CBN #NoFilter follows the life of Hightail, a professional hacker who attempts to penetrate a system to identify its security vulnerabilities before they get exploited by criminals. The program witnesses this year's ROOTCON Hacking Conference, a gathering for the growing hacking community in the Philippines. ROOTCON founder Dax Labrador then details how the conference has escalated its significance in the advent of cyberattacks among companies. Lastly, Hightail details how his work affects his personal life, to the extent of keeping secrets from his relatives about the details of his job.
#TechSabado September 16, Radyo 5
Meet the Hackers, (ABS-CBN Patrol ng Pilipino (October 02, 2012)
Pinoy shows Facebook hacking skills, (ABS-CBN Bandila) (September 18, 2012)
Pinoy Hackers We're Good Guys, (ABS-CBN Bandila) (September 7, 2012)
Privacy Policy
January 1, 0001
Readme
General Info
ROOTCON is solely owned by ROOTCON Communications, and a registered trademark of ROOTCON Communications. It is ROOTCON Communication’s policy to respect your privacy regarding any information we may collect while operating our website. This Privacy Policy applies to https://www.rootcon.org (hereinafter, "us", "we", "https://www.rootcon.org", "ROOTCON", or "ROOTCON Communications"). We respect your privacy and are committed to protecting personally identifiable information you may provide us through the Website. We have adopted this privacy policy ("Privacy Policy") to explain what information may be collected on our Website, how we use this information, and under what circumstances we may disclose the information to third parties. This Privacy Policy applies only to information we collect through the Website and does not apply to our collection of information from other sources.
This Privacy Policy, together with the Terms and conditions posted on our Website, set forth the general rules and policies governing your use of our Website. Depending on your activities when visiting our Website, you may be required to agree to additional terms and conditions.
Website Visitors
Like most website operators, ROOTCON collects non-personally-identifying information of the sort that web browsers and servers typically make available, such as the browser type, language preference, referring site, and the date and time of each visitor request. ROOTCON's purpose in collecting non-personally identifying information is to better understand how ROOTCON's visitors use its website. From time to time, ROOTCON may release non-personally-identifying information in the aggregate, e.g., by publishing a report on trends in the usage of its website.
ROOTCON also collects potentially personally-identifying information such as name, job title, company name, mobile number, phone number and or email address when the user registers for the ROOTCON events.
Gathering of Personally-Identifying Information
Certain visitors to ROOTCON's websites choose to interact with ROOTCON in ways that require ROOTCON
to gather personally-identifying information.
The amount and type of information that ROOTCON gathers depends on the nature of the interaction.
For example, During event registration, requesting letter invites, requesting approval letters, and other ROOTCON letter templates.
Security
The security of your Personal Information is important to us, but remember that no method of transmission over the Internet, or method of electronic storage is 100% secure. While we strive to use commercially acceptable means to protect your Personal Information, we cannot guarantee its absolute security.
Advertisements
Ads appearing on our website may be delivered to users by advertising partners, who may set cookies. These cookies allow the ad server to recognize your computer each time they send you an online advertisement to compile information about you or others who use your computer. This information allows ad networks to, among other things, deliver targeted advertisements that they believe will be of most interest to you. This Privacy Policy covers the use of cookies by ROOTCON and does not cover the use of cookies by any advertisers.
Links To External Sites
Our Service may contain links to external sites that are not operated by us. If you click on a third party link, you will be directed to that third party's site. We strongly advise you to review the Privacy Policy and terms and conditions of every site you visit.
We have no control over, and assume no responsibility for the content, privacy policies or practices of any third party sites, products or services.
Firewall
ROOTCON's firewall logs are used for debugging and or detecting attacks against ROOTCON services.
Servers
ROOTCON's servers does not store any personal information from our visitors and or our conference attendees. We also perform periodic updates, security testing and
patching of our servers.
Aggregated Statistics
ROOTCON may collect statistics about the behavior of visitors to its website. ROOTCON may display this information publicly or provide it to others. However, ROOTCON does not disclose your personally-identifying information.
Third party services
Lazada - ROOTCON sells it's merchandise through ebay, if you purchase something from ebay you adhere to ebay privacy policy[1].
Eventbrite - ROOTCON event registration is through Eventbrite, during sign-up you adhere to Eventbrite privacy policy [2].
Google Cloud - ROOTCON uses Wufoo forms for letter requests and other registration such as mini-events, during sign-up you adhere to Wufoo privacy policy [3].
Cookies
To enrich and perfect your online experience, ROOTCON uses "Cookies", similar technologies and services provided by others to display personalized content, appropriate advertising and store your preferences on your computer.
A cookie is a string of information that a website stores on a visitor’s computer, and that the visitor’s browser provides to the website each time the visitor returns. ROOTCON uses cookies to help ROOTCON identify and track visitors, their usage of https://www.rootcon.org, and their website access preferences. ROOTCON visitors who do not wish to have cookies placed on their computers should set their browsers to refuse cookies before using ROOTCON's websites, with the drawback that certain features of ROOTCON's websites may not function properly without the aid of cookies.
By continuing to navigate our website without changing your cookie settings, you hereby acknowledge and agree to ROOTCON's use of cookies.
Privacy Policy Changes
Although most changes are likely to be minor, ROOTCON may change its Privacy Policy from time to time, and in ROOTCON's sole discretion. ROOTCON encourages visitors to frequently check this page for any changes to its Privacy Policy. Your continued use of this site after any change in this Privacy Policy will constitute your acceptance of such change.
Third party privacy policy reference
[1] https://www.lazada.com.ph/privacy-policy/
[2] https://www.eventbrite.com/help/en-us/articles/460838/eventbrite-privacy-policy/
[3] https://cloud.google.com/terms/cloud-privacy-notice
Updated: Sat May 30 20:28:20 PST 2026
Revisions: 2db14b313fd834a77cb3a404d657d86cc02401e4
ROOTCON 1 Archives
January 1, 0001
Google Hacking
by: semprix
Google being the an angel and a demon, know the basics of Google Hacking.
(PDF)
Network Recon Basics
by: semprix
Know your target before anything else.
(PDF)
AV Is Dead! Is AV Dead?
by: Berman Enconado
(PDF) (Video)
We see it on the news, social media and ads.
Over the course of the past decade, the internet has been plagued by the boom of malicious programs.
Malware has continually evolved over the years to thwart every single technology that gets thrown at it.
Sad to say, AV is always on the reactive side of catching them.
Many companies are opting to switch to more advanced ways of finding and removing these malware.
But is trashing our AVs and switching to another technology really the solution?
Or will this lead us to a pitfall that will enable the bad guys to gain the upper hand, again.
This research shows the untiring battles between software security companies and malware authors over the years.
This case will show that there is no single technology to stop all cyber threats.
Big Data Analysis Applied to Network Security
by: Wilson Chua
(PDF) (Video)
This session will present case studies that showcases the possibilities of using Big Data analytics tools and technics in the Network security domain.
Using tools like Tableau, Neo4J, RapidMiner, Knime, Gephi, massive volume of IP traffic can be easily digested and actionable insights can be extracted in a matter of minutes. The output can be visually engaging and understandable to c-level executives.
In addition to using descriptive analytics that help with digital forensics, the session will also be sharing Predictive analytics to showcase how big data analytics can proactively "predict" which IP addresses will be 'bad' even before they do anything. This output can be used in turn by 'alerts' or 'hot' list or exclusion lists.
Certificate Based Strong Client Authentication as a Replacement for Username/Password
by: Lawrence E. Hughes
(PDF)
(Video)
Username/Password Authentication (UPA) is trivial to hack today, even when used with SSL protected websites (e.g. keyboard sniffer). A username/password database on a server is a juicy tidbit for a hacker to do mass harvesting of credentials, for fun or profit. Cracking even hashed/salted passwords is not rocket science. Most passwords can be found on the most common 10,000 list. Humans are notoriously bad at coming up with good passwords, and even those can be discovered. Now completely ineffective.
SSL/TLS has been around for a number of years, and provides good server to client authentication (you know you are connected to Amazon.Com’s server), and securely exchanging a symmetric session key (for encryption), but today most sites and apps are still using UPA for client to server authentication. Encrypting it helps against script kiddies but not against a competent hacker. 2FA (e.g. SMS or OTP token) helps, but does not prevent attacks on UPA. To be honest, for the most part Amazon could care less who YOU are, so long as your credit card payment clears. Other sites (like banks) care very much who you are. They don’t want some dude in Kazakhstan named Gregor emptying your account.
Fortunately, there is another part of the SSL/TLS handshake that is a very powerful replacement for UPA. It isn’t just a bandaid for a badly broken scheme (like 2FA), it replaces that broken scheme completely.
ComeLEAK - from hacking to behind bars
by: ROOTCON Crew
(PDF)
(Video)
ComeLEAK - You want to get an insight what really happened?
Weeks before the Philippine Election a group of hackers made their way inside the comelec's website and leaked a massive voters data to the public, It was then tagged as the worst public data breach in the Philippines.
ROOTCON remained silent as we want to be neutral and we don’t want to provide false information to the public. After doing some investigative-research we will be presenting the facts and testimonials, giving you deep dive insights on what really happened from hacking to behind bars.
This talk is based on the research done by the ROOTCON crews.
Cyber Security Threats in Digital Advertising
by: Mark Ryan Talabis
(PDF)
(Video)
This presentation is a first-hand investigation from a security practitioner of the unique security challenges and issues facing the multi-billion dollar digital advertising industry. The presentation is a detailed look of the intricacies of the advertising ecosystem, the advent of programmatic advertising, the economics of advertising fraud, and the rise of non-human traffic and malicious content that is currently plaguing the industry. This talk will include but is not limited to:
• The Digital Advertising Ecosystem and Programmatic Advertising – A primer on the digital advertising industry for the security practitioner.
• Convergence with Security – The security challenges and issues facing the digital advertising industry.
• Publisher Based Ad Fraud, Traffic Generators, Marketplaces and Exchanges – An introduction to the world of fake traffic and digital advertising fraud.
• Malware, Bots and Non-Human Traffic – Role of bots and malware in the digital advertising world.
Demystifying A Malware Attack
by: Christopher Elisan
(PDF)
(Video)
The media reports different malware attacks, different lamentations from those affected and different opinions of industry experts. What is lost in the conversation is the background: how are these attacks started, what are the different recipes of successful attacks and who are behind them. This talk will present what goes on in an attack and the different technologies and people involved.
Exploiting Home Routers
by: Eskie Cirrus James D. Maquilang, C)PEH
(PDF)
(Video)
And Jesus said “Why do you look at the speck of sawdust in your brother’s eye and pay no attention to the plank in your own eye?”
- Matt 7:3
Lots of us are looking for VULNERABILITIES anywhere, sites, systems, programs, other networks, other wifi. But have we checked our HOME for vulnerabilities?
Home Routers has lots of vulnerabilities and has GREAT potential in documenting vulnerability researches for CVEs. I will show you some remote SSID Changing using malicious website, Denial of Service, XSS, and getting router credentials.
Halcyon – A Faster Way to Build Custom Scripts for Nmap Scans
by: Sanoop Thomas
(PDF)
(Video)
Halcyon is the first IDE specifically focused on Nmap Script (NSE) Development. This research idea was originated while writing custom Nmap Scripts for Enterprise Penetration Testing Scenarios. The existing challenge in developing Nmap Scripts (NSE) was the lack of a development environment that gives easiness in building custom scripts for real world scanning, at the same time fast enough to develop such custom scripts. Halcyon is free to use, java based application that comes with code intelligence, code builder, auto-completion, debugging and error correction options and also a bunch of other features like other development IDE(s) has. This research was started to give better development interface/environment to researchers and thus enhance the number of NSE writers in the information security community.
Halcyon IDE can understand Nmap library as well as traditional LUA syntax. Possible repetitive codes such as web crawling, bruteforcing etc., is pre-built in the IDE and this makes easy for script writers to save their time while developing majority of test scenarios.
Ransomware: Battling A Rapidly Changing And Booming Industry
by: Jaaziel Sam Carlos
(PDF)
(Video)
The first cases of ransomware infection were seen in 2005. This Ransomware is known as PGPCODER that blackmails victim into paying $100-$200 for the decoder mail. In 2013, ransomware continued to evolve with the rise of Cryptolocker, a ransomware that encrypts files in a system using AES +RSA encryption making it virtually impossible to decrypt without a private or master key.
During this year 2016, several notable ransomware variants have emerged in the wild. Among them include a ransomware that locks the system from the Boot Sector; a crypto-ransomware variant with a ‘voice’ capability; and a ransomware that have employed a live chat service where a victim can negotiate or ask questions to the threat actors.
This paper aims to discuss about the latest trends in the ransomware industry. It will cover the newest extortion techniques and the most common entry vectors employed by ransomware. We will also present indicators of possible ransomware attacks, and more importantly, how users can protect themselves with the existing solutions against Ransomware.
Remote code execution via Java native deserialization
by: David Jorm
(PDF)
(Video)
Java's native serialization mechanism does not expose the same obvious RCE vectors as Python Pickle or XStream, and as such it is widely adopted in both commercial and open source applications. It does, however, expose RCE if certain conditions exist in classes on the server's classpath. This presentation will explain these conditions in detail, examine several instances of vulnerable classes in major Apache components, demonstrate exploitation, and provide best practices to avoid vulnerability.
Reversing Swift Apps
by: Michael Gianarakis
(PDF)
(Video)
Since it's introduction at WWDC in 2014 Swift has progressed significantly as a language and has seen increased adoption by iOS and OSX developers. Despite this, information pertaining to reverse engineering Swift applications is sparse and not openly discussed. This talk will dive into the Swift language and explore reverse engineering Swift apps from a security perspective. Topics that will be covered include quick intro to Swift from a pen testers perspective, various methods for obtaining class information from Swift binaries, Objective-C/Swift bridging, Swift runtime manipulation and function hooking.
Shifting Paradigms from Windows to Mac
by: Nicholas Carlo T. Ramos
(PDF)
(Video)
Much has been said about Apple and Mac users being less prone to security and malware attacks, leading them to have this false sense of security with regard to their devices. We know that this is no longer the case; based on the National Vulnerability Database (NVD) in 2014, Mac OS X has the most number of vulnerabilities reported among all operating systems, with four times the number of vulnerabilities compared to those reported on Microsoft Windows 7. A recent example is the DYLD_PRINT_TO_FILE vulnerability which when exploited enables attackers to gain root-level access to your Mac. As more vulnerabilities are exposed, Mac malware will continue to increase the way its market share is increasing as well.
Since most malware and threat actors have long been acting on the “old” stage--the Windows platform, reverse engineers and security analysts may also be accustomed to malware analysis for Windows. Mac OS X analysis is an arena that still waiting to be developed, and transitioning from Windows to Mac OS X treat analysis entails familiarity with Mac’s file formats, directory structure, processes, tools, and other artifacts. One also needs to ask how some common Windows malware routines such as terminating processes, redirecting URLs, disabling firewalls, and hiding files can be performed on Mac OS X.
This paper aims to help Windows users or those who are starting to explore Mac to make that shift. It will discuss Mac OS X file formats and well-known security features, as well as give deeper understanding on how malware can take advantage of the platform. It will compare artifacts that threats commonly abused on Windows with their counterparts on Mac, and provide information on the persistence methods malware can use. Lastly, it will discuss the latest notable Mac malware, the rise of Potentially Unwanted Applications (PUAs), Windows versus Mac OS malware trends, and the future of Mac threats.
Tranewreck
by: Jeff Kitson
(PDF)
(Video)
This talk covers the reverse engineering and exploration of the Trane ComfortLink thermostats. These devices are manufactured and produced by Trane, a popular heating and cooling company offering Zwave and WiFi enabled thermostats packaged with their appliances. This talk covers a vulnerability in the Trane ComfortLink thermostats that allows for remote manipulation and information extraction by an attacker. The devices are vulnerable by default and this talk addresses the physical dangers posed by this vulnerability to customers. The tools and methods used in finding this vulnerability are also discussed at-length in the presentation along with a video demonstration of the exploit in action.
ROOTCON 11 Archives
January 1, 0001
Breaking into the iCloud Keychain
by: Vladimir Katalov
(PDF) (Video)
Do you remember 'celebgate'? Well, iCloud is not just about backups and private pictures. There is quite a lot of data that is also being *synced* across all the devices, and so stored in the iCloud. iCloud Keychain (that keeps your passwords and credit card data) is the most protected data among all other iCloud-synced categories, but still there is a way to break into it, and funny enough, it is *easier* for the accounts with two-factor authentication enabled.
ROOTCON 12 Archives
January 1, 0001
Apple Health
by: Vladimir Katalov
(PDF) (Video)
Your heartrate and sleeping habits. Cardio and workouts. Steps and walking routines, and even your doctor’s recommendations are now known to Apple – and law enforcement. Turn your iPhone into a personal surveillance device tracking your entire life – and sharing it with the cloud. Learn what gets stored in iCloud and how to extract and analyse health data. Warning: don’t try it on your partner’s iPhone to avoid disappointment.
ROOTCON 13 Archives
January 1, 0001
APAD: An EDR Grade Agent for Wi-Fi Access Points
by: Vivek Ramachandran
(PDF) (Video)
Wi-Fi is ubiquitous and the de facto way to connect to the Internet. With increasing Wi-Fi speeds and the gradual disappearance of the network port on our laptops, it might soon be the only way. Being entrusted with such an important responsibility, one would assume that Wi-Fi access points would have sufficient built-in security and attack detection. Unfortunately, this is farther away from the truth as it could be! Wi-Fi access points in the personal and SMB space have barely evolved over the past decade! This puts users at great risk - we routinely hear about attackers redirecting DNS and other traffic, attacking users behind an access point, etc. One would ask - why are the Access Point vendors not doing anything about this? Simple answer: hardware vendors typically don’t care much about software. So, we’ve decided to take matters into our own hands :)
In this talk, we will be releasing - Access Point Attack Detector (APAD): an enterprise-grade access point monitoring agent built from the grounds up. APAD will have a kernel and user mode components which will continuously monitor your access point platform for attacks and intrusion attempts! The tool should be easily portable to most Linux based access point platforms. For our demo - we will be using OpenWRT along with a hardware access point! Enough said - looking forward to seeing you at the talk!
ROOTCON 14 Archives
January 1, 0001
2 wires and 2 wheels: Bikes can do CAN too
by: @canbusdutch
(PDF) (Video)
"Most motorcycle manufacturers started using CAN in the early 2000s, and since then, more and more devices have been added to CAN networks on bikes. ABS, traction control, navigation systems, luxuries like heated grips, basics like lighting and advanced diagnostics, but for some reason, they still haven’t grabbed the attention of car hackers. Why? I hope to open the door to this field, and help gain popularity in motorcycle CANbus hacking.
Through this adventure, you’ll follow me as my passion for motorcycles, goes headfirst into my passion for computers, and I build tools and software to reverse engineer my motorcycle's CAN system.
Python scripts, microcontrollers, pulse width modulation, some potentiometers, and a bit of what I like to call “Ruthless Engineering”, has helped me finally reach the pinnacle of CAN bus packet reversing.
We’ll cover some engine simulation, execute some packet capture session analysis, and put it all back together again, for the development of an aftermarket gauge cluster."
ROOTCON 15 Archives
January 1, 0001
ROOTCON 15
Theme: (Hard Wire)
October 13, 14, 15, 2021
Zoom Webinar, Discord
Media direct downloads || YouTube Videos
Talks
Attacking Modern Environments Series: Attack Vectors on Terraform Environments Inbox
by: Mazin Ahmed
Ever come across an environment in an engagement that uses Terraform for IAAC (infrastructure-as-
code) management?Almost every modern company does now.
In this talk, I will be sharing techniques and attack vectors to exploit and compromise Terraform
environments in engagements, as well as patterns that I have seen that achieve successful infrastructure
takeover against companies. I will be also covering detection and prevention methods for each attack vector discussed in my talk.
This is part of my work-in-progress research in cloud security and attacking modern environments.
Burnout: The Security Risk
by: Chloé Messdaghi
Did you notice a shift in your mental health and/or your colleagues? Burnout was at an all time last year due to the surreal 2020. As we approach the end of the pandemic, we recognize how critical mental health plays when accomplishing goals and productivity output. This talk dives into the factors that lead to burnout among security professionals, the clear line between burnout and failure to retain team members, and how to invest in your team to make sure your team is able to thrive during stressful times.
Buzzard : Crafting your post exploitation framework against odds
by: Aravindha Hariharan
and
Subhajeet (ElementalX)
Quality & Innovation over quantity. Post-exploitation is a crucial part of red-team assessment as the other phases can be carried out passively but not post-exploitation. Also one of the very important aspect of this entire process of this maintaining access to the compromised host should be leveraged with keeping stealth in mind starting from performing enumeration to leveraging administrator level privileges and lateral movement, as modern day sophisticated EDRs and SIEM solutions and other detection engineering based software aim on staying ahead detecting these malicious implants & beacons. However in this game of cat & mouse the conventional part of red teaming also involves discovering bypass techniques for all the security mechanisms deployed. Once the red teamer gains an initial foothold into the host, he can implants an adversary in the host to achieve persistence. The adversary is capable of staying dormant and performing operations in stealth. It is capable of operating without internet access and can send data or receive commands when connected to the internet. This happens via the command and control server of the red teamer. It is crucial that the command and control server is secure and fast to reduce latency and improvise data transmission. Above all, the server must be easy to deploy and maintain and must be user-friendly, in a few instances the red teamer might have to pivot the data through another internal system that is connected to the internet. During such conditions, the C&C server must stay as it is crucial that the C&C server stays light, fast too Buzzard which is built by two undergrad students has been developed to operate under such intense circumstances, easy to deploy, with both command line and web interface giving the user the freedom to choose the beacons and implants of his own choices, as buzzard aims to provide implants programmed using C, Python, Rust, Go. Although some of the implants & beacons are built upon languages which are not "write once & run everywhere" we aim to build small additional beacons which helps to get all necessary feasible environment which helps other beacons for easy execution.
Buzzard is a hybrid architecture that is put together into a docker container. We have a web interface where the attacker interacts to manipulate tasks according to the requirements. The Web front-end is made up of HTML, CSS, and Jquery, it serves through Node JS which acts as a middleware between REST API and the front-end. The API follows the principle of CRUD(Create Read Update Delete) which is a function like a stateless API and connects to a MongoDB database to store and retrieve information about the tasks. The API also serves the beacons directory for sharing the scripts which interact through the implant. We have a dedicated module that is defined to create tunnel sessions.During each session creation a unique URL is created and some beacons are depended on it, which is dynamic modified to the respective files. When the server is stopped, it will be
rewritten back to default. We have a separate module that creates a channel for WebSocket connection for updating real-time notification about the task as well it is used to update the target page for online status. The Monitor module is a multi-thread module to run in the background to check the status of the target machine and update the profile page whether the respective target machine is online or offline by sending an ICMP packet to the target and checks for the status of the machine.
Buzzard currently supports 9 post-exploitation modules and more to be added. Regarding providing a multi-platform support, the implants are only capable on running in Windows & Linux machines . Therefore buzzard is a flexible, easy to deploy, monitor and user friendly C2 server with a support providing the user a choice to choose it's favorite programming language for beacon making it easy for him to debug them . The main goal still remains to make the beacons more persistent and making it more user-friendly & applying anti-reverse engineering traits making it a bit tougher for the defender to analyze these beacons.
Click Here For Free TV! Chaining Bugs to Takeover Wind Vision Accounts
by: Leonidas Tsaousis
Wind Vision is a streaming service offered by a top Greek telecommunication vendor. With over 40.000 active subscribers, a user can just download the Android application and watch TV from anywhere ...And so could a malicious third party, by exploiting a series of vulnerabilities to go from one wrong click by the user - to complete takeover of their account. This talk will present the findings of independent research conducted in 2020 that led to the discovery of several bugs which, although posing low-impact individually, they could result in a much greater attack when chained together.
We will dive deep into the analysis of the vulnerabilities, discussing the common mobile development pitfalls and the psychology behind confusing prompts. Attendees will also have the chance to install the demo Proof of Concept malware application that was developed (it's safe, I promise) to see for themselves how the full chain worked. Mobile developers in the audience will gain insight into how to prevent such attacks, to create apps that are fun, but also keep their users' watchlists safe from targeted malware. Finally, we will close up with a review of the disclosure process, the aftermath of resolution, and other lessons learned that will hopefully set aspiring researchers on the right path to find vulnerabilities in products they use day-by-day.
The vulnerabilities were released in a technical advisory:
https://labs.f-secure.com/advisories/wind-vision
And the in-depth analysis was presented in a follow-up technical blog post:
https://labs.f-secure.com/blog/wind-vision-writeup
Crafting your own combat hardware
by: Luis Angel Ramírez Mendoza (@larm182luis) and Mauro Eldritch (@mauroeldritch)
In this talk, we would like to present two of our newest Hardware Hacking experiments.
Our Armory consists of all sorts of weaponized domestic hardware (BadUSB power banks, USB speakers, keyboards, and more) and infiltration devices, which are available as open-source projects. In this new visit to our Armory, we would like to showcase our newest tools: DIY Movement Sensors with integrated cameras for Physical Hacking and WiFi Deauther Charges. The sensors can be deployed while doing physical penetration testings or red teaming exercises, and are connected to the attacker's smartphone to give early warnings about any movement detected on the covered zone. The Electronic Charges are portable throwable devices, covered in a special adhesive coating which allows them to stick to ceilings or other surfaces. Upon being activated, a countdown starts and when it reaches zero, the device will start to run a pre-selected routine which can consist of WiFi deauthing floods, to bruteforcing, or even simply led-light flashing and making noise to attract attention. Demo videos will be shown during the presentation.
Main topics are Hardware Hacking and Hardware Programming.
Discovering C&C in Malicious PDF with obfuscation, encoding and other techniques
by: Filipi Pires
Demonstrate different kind of structures in the binaries as a PDF(header/ body/cross-reference table/trailer), explaining how each session works within a binary, what are the techniques used such as packers, obfuscation with JavaScript (PDF) and more, explaining too about some anti-disassembly techniques, demonstrating as a is the action of these malware’s and where it would be possible to “include” a malicious code. By the end of this “talk” it will be clear to everyone, differences in binaries structures, how can the researcher should conduct each of these kind of analyzes, besides of course, it should seek more basic knowledge, with file structures, software architecture and programming language.
Fuzzing: Revisiting Software Security
by: Nafiez
Software exploitation has been done for many years and the research keeps continuing, resulting in different types of attacks that have been approached to prove the issue in the software itself are breakable. Back in the early days of software exploitation, vendors kept denying vulnerability exists in their products and some took years to fix the problem. Until then, full disclosure was introduced to the public and everyone doing the same research keeps posting the exploits on the Internet and being abused either in a good or bad way.
Vulnerability research is one of the methods of securing a software that usually involves complex processes, such as reverse engineering, fuzzing, secure code auditing, developing proof-of-concept or could be a full chain exploit. These days, we can see many resources that could help in this process, including tools that can be used for fuzzing or even libraries to speed up exploit development. The speed of mitigations developed by giant tech vendors such as Microsoft has brought some attention to researchers and reduced many attack surfaces. With this, the cost of vulnerability research has slightly changed.
Disclosing vulnerability to a vendor could be a pain process, months of conversation over email, either with updates or no progress at all. In our talk, we will be discussing research that has been done on different types of software, including our approach and analysis. We will discuss the vulnerability we found and the exploitation strategy. To add some fun facts, we will talk about how we approach one of the Malaysia government agencies on coordinating vulnerability disclosure about software security.
Gathering Cyber Threat Intelligence from the Cybercriminal Underground
by: Eric Reyata
CTI focuses on data collection and information analysis so we can gain an insight about threats against our organization. An often overlooked, but very important source of intelligence is the Criminal Underground.
In this talk, we will discuss how to produce and deliver relevant, accurate, and timely curated information from the CU so that your organization can learn how to protect itself from a potential threat. We'll also look into data breaches, ransomware leak sites and criminal marketplaces to have a better understanding of the underground economy.
Hack the Planet! Desecuritise Cyberspace
by: Emil Tan
I'm in cybersecurity. You're in cybersecurity, or interested in cybersecurity. But, what are we securing? Are we getting better at it? In this talk, I'll deconstruct the concept of (cyber)security and discuss why and how hackers — you and I — should desecuritise cyberspace and hack the planet instead.
Keeping Up With Modern Automotive Exploitation
by: Kamel Ghali
It is common knowledge that vehicles are becoming more connected to the world around them with each passing year. Transportation itself is undergoing a connectivity revolution, with cars, trucks, trains, and even boats being synchronized into the increasingly IoT-influenced world. Appropriately, the global automotive industry and international legislative bodies have begun to prioritize the inclusion of cybersecurity measures into vehicles – passing regulations and industry standards to guide the future of connected transportation.
Despite these strides in awareness of the need for security in vehicles, we still see numerous instances of vehicles being remotely compromised every year. This research is almost always done in a benevolent, white-hat setting (thankfully) but recent disclosures in automotive security have highlighted the importance of security processes in the automotive and greater transportation security industry. This presentation aggregates the most significant vehicle security research presented in the past few years, draws valuable lessons from analysis of the types of attacks used and technologies targeted, and explores ways in which similar attacks can be prevented in the future by adhering to developing industry standards and global legislation.
Malware Hunting - Using python as attack weapon
by: Filipi Pires
The purpose of this presentation is to use python scripts to perform some tests of efficiency and detection in various endpoint solutions, during our demonstration we`ll show a defensive security analysis with an offensive mind performing an execution some python scripts responsible for downloading some malware in Lab environment. The first objective will be to simulate targeted attacks using a python script to obtain a panoramic view of the resilience presented by the solution, with regard to the efficiency in its detection by signatures, NGAV and Machine Learning, running this script, the idea is to download these artifacts directly on the victim's machine. The second objective is to run more than one python script with daily malware, made available by MalwaresBazaar upon request via API access, downloanding daily batches of malwares .
With the final product, the front responsible for the product will have an instrument capable of guiding a mitigation and / or correction process, as well as optimized improvement, based on the criticality of the risks.
OAuth Authentication Bypass
by: Sheikh Rizan
Overview
OAuth is an open standard for access delegation, commonly used as a way for Internet users to grant websites or applications access to their information on other websites but without giving them the passwords. We often see websites with “Sign in with Facebook” option. This facility provides convenience to the users that do not wish to sign up using the traditional username and password option. However, there exist a small number of websites that have poorly implemented OAuth allowing an attacker to bypass the authentication and impersonate another user to gain access to websites’ protected resources. This technique is known in the Bug Bounty community and is regarded as an authentication bypass or an account take-over. While there are various write-ups with regards to OAuth authentication bypass, this technique is not widely covered. We would like to present the technical details of the vulnerability we had found.
Details
During this talk, we will present technical findings pertaining how this exploit works. We will show screenshots of traffic intercepted in Burpsuite and which parameters are tempered by the attacker to gain an account take-over. When successful, an attacker will be able to impersonate another user and will be able to access the protected resource on the Resource server. The incorrect implementation of OAuth to authenticate users could lead to unauthorized access containing sensitive PII user data. This vulnerability is trivial to exploit and identify, a well-trained web penetration tester should be able to spot this vulnerability during a black box test and make recommendations to rectify the problem. It is important to summarize that the fault is not within the Authorization Server (Google, FB or Twitter) but rather due to the failure of the Resource Server to properly validate certain parameter. It is imperative that the Resource server never trust any user supplied parameters.
Phishing & Education: Applying security principles during the pandemic
by: IJ Puzon
Based on a true story, it details the analysis of an email phishing attempt against an ordinary Filipino, an understanding of why the threat of phishing is common and the application of security principles by an educational institution during the pandemic.
Securing Process Control Data Transmission to the Blockchain Network
by: Lloyd Kenneth Tugbo
and
Arian Hills
Integrating Blockchain into Industrial Control Systems (ICS) offers several benefits, but securing its data is a significant issue. This concern slowed the development of this technology in the ICS Industry, preventing it from achieving the level of disruption seen in other industries such as electronic gaming and finance. While encryption is a secure technique in and of itself, it is insufficient to address the data privacy issue inherent in data transmission to the blockchain, rendering it unsuitable for use in the industrial sector where process control data is critical. End-to-end encryption is seen as a solution for L3 to the Blockchain network; however, the optimal end-to-end implementation from the Purdue model's L0/L1 to L3 remains a study topic. This paper will examine existing technologies that can be chained to enable simple and secure transfer of plant data from L0/L1 to Internet Blockchain networks.
To integrate Blockchain in ICS, we considered embedding a blockchain inside a plant network; however, this approach is appropriate for a different use case. The second option is to build a framework around existing technologies. We begin by identifying the main issue that requires attention, which is securing the data transmission. The issue we identified is with data transfer from the Purdue Model's L0/L1 to the Blockchain network and the study examined a variety of potential solutions to this issue. End to End encryption was chosen as the primary method of connecting L3 to Blockchain, either through the use of pre-existing E2EE messaging protocols such as Matrix or through the development of a new E2EE protocol that meets the blockchain and ICS integration criteria in the L3 to Blockchain network chain. These E2EE solutions are limited to L3 to Blockchain networks, which means that there are still issues with E2EE for devices in L0/L1 networks up to Level 2.5 of the Purdue Model, for which we introduced the concept of developing E2EE protocols for embedded devices such as the E4, which is still in its early stage of development and thus not widely used by device manufacturers. Additionally, we recommend the FDI Technology end-to-end solution, which securely connects plant devices to business layers through the use of digital signature technology in the plant devices and secure data transfer via the OPC UA messaging protocol, which is used in the L2.5/3 layer. Although this technique does not utilize end-to-end encryption, we can guarantee that it is not tampered with during transmission due to the digital signature and timestamping features. A sample architecture was presented in which two technologies were integrated. To begin, we'll use Matrix as an E2EE solution for safe data transfer from L3 to Blockchain, followed by FDI technology for securely transmitting data from L0/L1 to L3 network to complete the end-to-end solution.
Skrull Like A King: From File Unlink to Persistence
by: Sheng-Hao Ma
The king is dead, long live the king! There is a well-known feature by which anti-virus or EDR can capture ambiguous or suspicious program files and send them back to security response center for researcher analysis. For malware designers, playing cat and mouse with security solutions in the post exploitation stage while hiding their backdoors from malware detection and forensics is a crucial mental challenge.
Many methods used in the wild by hackers against researchers have already been discussed, for example using a COM hijack to obscure their malware, deploying a kernel hook-based rootkit, bypassing signature-based scanning, and others besides. There's still no method robust enough to counter these techniques, as researchers often cannot totally understand how the malware works internally even if it's caught and analyzed.
Imagine a situation: malware acquires DRM protection, and thereby naturally damages itself when copied from the infected machine. Is it possible? How would it happen? In short, security vendors should be prepared to handle this situation within the Maginot line of their own defenses.
In this talk, we are going to share a breakthrough discovery obscured from even the most through researchers, which can be weaponized and used in the wild with wide applications. We'll show how it links up three different vulnerabilities, and is then weaponized to form three different methods of abuse. At the end of our talk, we'll live demo three proof-of-concepts, share our source code, and propose several mitigation plans for security vendors.
1. Well-Known Methods of Post-Exploitation (~3min)
- Techniques for Hiding Malware: COM Hijacking, Rootkits and More
- Anti-Debuggers, Sandboxes, Virtual Machines, and Custom Packers
- Masquerade Methods: Hollowing, Doppelganging, and Herpaderping
- Defects in current techniques
2. NTFS Abuse Features in Windows (~13min)
- Alternate Data Streams (ADS)
- How Windows Locks Exe Files of a Running Process
- Abusing ADS to Unlink the Exe File of a Process
- (Demo) Remove The Exe File from a Running Process (Like a Fileless Attack)
- (Demo) Woohoo! We're signed by Microsoft ;)
3. Win32 Application Loader Features (~10min)
- Application Loader Task to Fix Up PE Image in Dynamic
- Import Table & Win32 ABI by Function Ordinals from the Compiler
- (Demo) Designing Malware DRM: Homogenize Backdoors' Import Table with a Victim's ABI
4. Conclusion (~4min)
- Doppelganging vs. Herpaderping vs. Skrull
- Patch Suggestions & Mitigation for Security Vendors
- Closing Remarks
The Curious case of knowing the unknown
by: Vandana Verma Sehgal
Modernisation the applications is the need of the hour. However, we still see the vulnerabilities that keep creeping in. When the loopholes in applications (such as legacy, desktop, web, mobile, micro services) are exploited, it can give threat actors visibility and access to the organisation’s data.
As per one of the research 96.8% code on the internet is OpenSource. When Open Source is eating up the whole internet. It becomes imperative to know the aspects of the open source’s usage, if the open source libraries are not used properly or updated on time, open source can make the applications severely vulnerable. With the talk, we will find the hidden treasures with open source projects and will try and see how we can find them before someone else finds it.
The Kill Chain: Future of Cyber in Defense
by: Harshit Agrawal
Modern military forces rely heavily on a variety of complex, high technology, electronic offensive, and defensive capabilities. A well-timed Tweet, an errant Facebook group, or a seemingly harmless WhatsApp forward holds the potency to be even more dangerous than artillery fire and airstrikes. This session aims to reflect the opportunity for attendees to learn about emerging technologies, threats, and practices that will shape the future of warfare and cyberspace operations.
The main topics are Information Warfare, Cyber Reconnaissance, Internet of Battlefield Things. This session will introduce attendees to the Era of Convergence of Cyber and EW, Operations in Multi-domain, along with case studies of Cyber-Reconnaissance, C-UAS, Space warfare, and a glimpse of future warfare from a technological perspective (IoBT).
Using Wordpress comments section as a C&C for fun
by: Juan Karlo Licudine (accidentalrebel)
I explore the possibility and feasibility of using the comments section of abandoned Wordpress-powered blogs as command and control servers. There would be no site take-over nor use of APIs. Communications will be done by disguising commands as legitimate comments or as spam. I'm sharing this as a fun experiment with a novel approach to C&Cs that can offer anonymity with zero hosting costs.
Speakers
An experienced python developer and student by day & offensive security researcher by night. I love to make tools focused on offensive security, and I love to tinker around web exploitation & reverse engineering.Currently a part of AX1AL reverse engineering community.
ROOTCON 16 Archives
January 1, 0001
ROOTCON 16
Theme: (Hard Wire)
September 28, 29 & 30 2022
Taal Vista Hotel, Tagaytay City
Media direct downloads || YouTube Videos
Talks
A new secret stash for fileless malware
by: Denis Legezo
Download Slide |
Watch Video
Today, attacks using fileless malware have become more complex and the actors behind them have created new advanced means of implementing them. In 2022, Kaspersky discovered the new methods used to keep the code hidden from prying eyes. For the first time, we’ve discovered that Windows’ event logs participate in the infection chain. This is concerning, as the event logging exist in any installation of the most widely used operating system on the globe.
These informational messages might keep the additional binary data. The dropper saves the shellcode into the Key Management System’s (KMS) event sources information, assigning a specific category ID and incremented message IDs. Auxiliary malicious modules can then gather 8KB pieces from logs, turn these into a complete shellcode and run them.
Nevertheless, the actor’s interest in the event logs isn’t limited to just keeping the shellcodes. To hide the infection process, Go droppers also patch the ntdll.dll Windows API functions related to logging (like EtwEventWriteFull, etc.).
In our presentation, we will share the results of our in-depth research into the infection chain, containing:
- commercial pentesting frameworks
- a number of anti-detection decryptor-launchers, written in different languages
- last stage fully-fledged trojans for C2 communications and lateral movement
Alternative ways to detect mimikatz
by: Balazs Bucsay / @xoreipeip
Download Slide |
Watch Video
mimikatz is detected by AVs and EDRs in different ways, mostly based on signatures and behavior analysis. These techniques are well known, but we looked into a few other things to find more exotic ways. Turns our that mimikatz by default talking to USB devices, so I created an emulated device as a user-mode driver for Windows, which is capable to detect most mimikatz variants out-of-the-box. Other technique was implemented and will be part of the presentation, where the console communication is "sniffed", but this technique can be applied to other malware as well. Both techniques will be published and code will be opensourced after the con.
AWSGoat : A Damn Vulnerable AWS Infrastructure
by: Jeswin Mathai, Shantanu Kale,
and Sanjeev Mahunta
Download Slide |
Watch Video
Compromising an organization's cloud infrastructure is like sitting on a gold mine for attackers. And sometimes, a simple misconfiguration or a vulnerability in web applications, is all an attacker needs to compromise the entire infrastructure. Since cloud is relatively new, many developers are not fully aware of the threatscape and they end up deploying a vulnerable cloud infrastructure. When it comes to web application pentesting on traditional infrastructure, deliberately vulnerable applications such as DVWA and bWAPP have helped the infosec community in understanding the popular web attack vectors. However, at this point in time, we do not have a similar framework for the cloud environment.
In this talk, we will be presenting AWSGoat, a vulnerable by-design infrastructure on AWS featuring the latest released OWASP Top 10 web application security risks (2021) and other misconfiguration based on services such as IAM, S3, API Gateway, Lambda, EC2, and ECS. AWSGoat mimics real-world infrastructure but with added vulnerabilities. The idea behind AWSGoat is to provide security enthusiasts and pen-testers with an easy-to-deploy/destroy vulnerable infrastructure where they can learn how to enumerate cloud applications, identify vulnerabilities, and chain various attacks to compromise the AWS account.
Building defensive playbooks from others misfortune
by: Chester Wisniewski
Download Slide |
Watch Video
Building defensive strategies is difficult at the best of times and too often is confused by what we read in the headlines,
instead of from real hands-on experience. The problem with getting the experience is that you must be victimized to gain
the experience necessary to craft your defensive plans. We must learn from others to gain the experience we need before it
happens to us.
Sadly, most victims don't share their stories as they are often embarrassing or show some level of negligence in keeping
their data secured. This talk will condense the experience of those victims into actionable advice for defenders to use in
creating their own up-to-date defensive strategies. Using the data from 144 distinct attacks in 2021, I will demonstrate
the most common tools, tactics, and procedures (TTPs) used to gain access to networks and the behaviours to watch for that
indicate compromise. This information was gathered by the Sophos Rapid Response team, a group of incident responders who
are called in to assist victims during attacks worldwide.
China’s Cyber Capabilities: Espionage, Warfare, and Implications
by: Aaron Aubrey Ng
Download Slide |
Watch Video
Over the past decade, there has been an alarming rise in the frequency and sophistication of China’s state-sponsored and state-affiliated cyberespionage activity, as well as its scope of targeting. China-Nexus Adversaries have deliberately and aggressively pursued targets across a spectrum of industries, including technology, defense, energy, healthcare, education, and other key sectors in pursuit of trade secrets and of sensitive information.
Of note, in early 2021, the China-Nexus Adversaries rapidly and effectively exploited a series of vulnerabilities in Microsoft Exchange — now collectively known as ProxyLogon and ProxyShell — to compromise email servers and consequently the sensitive information of tens of thousands of organizations around the world. Over the duration of the pandemic, Chinese cyberespionage campaigns continue to target hospitals and research institutions for data that could confer competitive advantages in science and technology, and at the same time, demonstrating emphasis on COVID-19 related research.
Coupling these recent prolific intrusions with the longstanding campaign of targeting a wide swarth of industries, including insurance, travel & hospitality, government, for the purpose of acquiring sensitive personnel data, the threat that China-Nexus Adversaries pose to organizations today cannot be understated.
This session will provide insight into China’s intent and capabilities for cyberespionage and importantly what organizations can do to address this challenge effectively.
DDexec
by: Carlos Polop (@carlospolopm) and Yago Gutiérrez
Download Slide |
Watch Video
Running binaries in memory from a reverse shell on the target machine is very common in Windows environments, there are dozens of different ways to achieve this and many of them very simple. However, in Linux environments it is not so common, nor so easy to load things into memory from a simple bash session, for example.
In this talk we will present and show a novel technique for loading binaries and shellcodes into memory from a linux session without the need to touch the disk, allowing not only to be potentially more stealthy, but also to bypass measures such as mounting the filesystem protected with read only and/or noexec.
Gazing into the Crystal Ball - The Fog of Cyberwarfare Escalations
by: Harshit Agrawal (@harshitnic)
Download Slide |
Watch Video
Every new technology presents the possibility of new weapons, and for every new weapon, there’s a soldier hoping it will yield the ultimate advantage, although few ever do.
The nature of war is never gonna change. But the character of war is changing before our eyes–with the introduction of a lot of technology, a lot of societal changes with urbanization,
and a wide variety of other factors. In order to have a robust discussion about how emerging technologies may affect the proliferation of modern cyberwar, it is vital to understand
these technologies. In this session, ISR techniques (intelligence, surveillance, reconnaissance), and counter-drone security serve as productive examples of technologies that we
have witnessed in recent conflicts playing the role of a potential tool of exploit and will be greatly escalated in the future as well. This session provides the background and context
required to assess potential challenges to this emerging cyber threat. As will be demonstrated with case studies, advancements in these areas are especially relevant because
they have made it increasingly easy for Infosys to leverage these technologies to achieve its objectives and threaten the global IT/ICS ecosystem.
How Did I Get Here? I still don’t know what I’m doing: Getting into The Lifelong Adventure of Learning Cybersecurity & Incident Response
by: James Kainth (@j3st3rjames)
Download Slide |
Watch Video
Where will your journey take you? My adventures have taken me from feeling confident about knowing what is normal for our computers or in our networks, to never feeling that way again and daring to innovate. Incident Response is an ever-growing field, with not enough people who can do the work. Heck, most jobs that require some form of cybersecurity are suffering from lack of support. The skills gap is REAL! If you want to learn and stay up to date with the ever-expanding world of cybersecurity, then this talk is for you. In digital forensics/incident response (DF/IR) you can peek behind the scenes of technology and learn about an entire world you never even knew was there! Think you’ve cleaned up after your ultimate hack? Think again! By starting your adventure into DF/IR you get to sleuth and learn about the artifacts attackers leave behind! Join me on this journey of self-improvement as we discover the potential cyber detectives we know we can be!
Learn what the necessary skills are to get into DF/IR with James Kainth who works on a Fortune 50 Incident Response Team! Develop an action plan to get started on your journey learning DF/IR Today!
While attending this session, folks will:
* Learn about the field of digital forensics & incident response
* Learn about ways to stay up to date in the cybersecurity industry
* Learn skills to tackle the imposter syndrome that comes along with being in any technical field
* Realize that Imposter syndrome can be a productive feeling if managed well
* Learn about free/open-source resources like Wazuh, ZimmermanTools, Autopsy, FTK Imager, Elastic Stack, Wireshark, and more!
* Generate an action plan and outline next steps to continue learning DF/IR
* Don’t delay … Start threat hunting today!
Human-Controlled Fuzzing With AFL
by: Maxim Grishin / Igor Korkin (@IgorKorkin)
Download Slide |
Watch Video
Early detection of new bugs is crucial for all modern software products. Fuzzing techniques are applied to reveal different types of bugs and vulnerabilities. American Fuzzy Lop (AFL) is a free most popular software fuzzer used by many other fuzzing frameworks. However, AFL has some disadvantages, the key one is that AFL verifies the program code without human intervention. However, involved security expert can make the fuzzing process more focused. On the one hand, AFL simplifies applying fuzzing systems, but, on the other hand, the flexibility of AFL is limited. Fuzzing is based on sending generated data as input to the target application and recording how the instrumented app processes this data. Using the output of the instrumented app, AFL can regenerate new input data to go deep inside the application into the next step.
As a result of such an autonomous mode of operation, a fuzzer spends a lot of time analyzing minor code sections. To solve this question, the paper proposes a new approach that can fuzz only the specified functions. As a result, the chosen ones will be inspected more meticulously by a fuzzer, without wasting the time on inspecting minor code sections. Another new feature is to provide feedback about the inspected functions and controls, so that an expert can change which code functions need work in runtime. The developed module has been integrated with AFL and successfully responds to this challenge. This expert-controlled fuzzing with AFL shows positive test results.
Microsoft Defender Will Be Defended: MemoryRanger Prevents Blinding Windows AV
by: Igor Korkin (@IgorKorkin) and Denis Pogonin
Download Slide |
Watch Video
Windows OS is facing a huge rise in kernel attacks. An overview of popular techniques that result in loading kernel drivers will be presented. One of the key targets of modern threats is disabling and blinding Microsoft Defender, a default Windows AV. The analysis of various attackers’ techniques that can disable and blind Microsoft Defender will be given. One of the recently published attackers’ techniques abuses Mandatory Integrity Control (MIC) and Security Reference Monitor (SRM) by modifying Integrity Level and Privileges for the Defender application via syscalls. However, this user-mode attack can be blocked via the Windows “trust labels” mechanism.
The presented research discovers the internals of MIC and SRM, including the analysis of Microsoft Defender during malware detection. We show how attackers can achieve the same result using a kernel-mode driver. The driver modifies the fields of the Token structure allocated for the Microsoft Defender application. The experiments prove that Microsoft Defender is disabled without triggering any Windows security features, such as PatchGuard. The customized MemoryRanger was used to protect the Windows Defender kernel structures. The experiments show that MemoryRanger successfully restricts access to kernel data from illegal access attempts with affordable performance degradation.
Pwnppeteer - Phishing Post {Exploi/Automa}tion at Scale
by: Joffrey Czarny aka Sn0rkY
Download Slide |
Watch Video
Phishing is well know attack but more and more company have implemented countermeasure to limit the efficiency of this kind of attack. For example, Multi-Factor Authentication (MFA) is being adopted to make password spraying and standard phishing ineffective. Countermeasures adopted raise the exploitation bar, for attacker.
But what happens if you can easily tamper MFA too? If you can proxy all traffic, directly steal sessions and automate malicious actions before the credentials are changed or the attack detected? What do you think if you phish an SSO portal and then you're able to instrument all applications granted with a SSO token...
The goal is to share my experience of a massive phishing campaign, how you can use Muraena/Necrobrowser at scale and show how we can phish and get a temporary access to steal enough data or add some persistents access in order to come back later. And of course before being detected and losing access.
Mureana/Necrobrowser tool and concept have been already presented in several conferences but what I plan to present here is Pwnppeteer - Necrobrowser Lambda implementation https://github.com/muraenateam/pwnppeteer. The focus will be done on targeting SSO portal and how this attack can be efficient.
Security Like the 80's : How I stole your RF
by: Ayyappan Rajesh
Download Slide |
Watch Video
The issue about convenience vs. security has been spoken about for years now, with most devices having wireless capability now, it invites trouble, especially when it is not encrypted or secured. Right from our tap-to-pay cards to even unlocking and starting out car.
This talk discusses CVE-2022-27254 and the story of how we came about discovering it. The CVE exploits an issues wherein the remote keyless system on various Honda vehicles, allowing an attacker to access the cars, and potentially even let them drive away with it!
Signs, Signs, Everywhere There are Signs of a Ransomware Intrusion
by: Allan Liska
Download Slide |
Watch Video
Threat hunting is great way for organizations with even a limited security budget to look for indications that a ransomware actor is in your network. However, there is an assumption that threat hunting is challenging and requires a large, well-funded security team to carry out. That is not always the case. There are some low-cost things organizations can do to conduct effective threat hunting missions in your network. This presentation will review some effective, relatively easy threat hunting missions that defenders can carry out to look for signs of a ransomware actor. Some of these include:
1. Alerting when security tools are disabled
2. Looking for remote desktop tools
3. Hunting through PowerShell logs
4. Traffic to mega.nz or one of its other domains
5. Looking for common file copy tools.
Streamline security with shift left: A cloud approach
by: Avinash Jain
Download Slide |
Watch Video
In the agile world, continuous iteration of development and testing happens throughout the software development lifecycle involving constant collaboration with stakeholders and continuous improvement and iteration at every stage, engineers release their changes very frequently. All this makes the chances of potential security loopholes more and more real.
According to the most recent Secure Code Warrior report, more than 50% of organizations are still following reactive security practices, such as using tools on deployed applications and manually reviewing code for vulnerabilities. Even the DORA 2021 Accelerate State of DevOps report suggests that security can no longer be an afterthought. Top performers who have implemented security practices earlier in the software development life cycle are likely to exceed their reliability targets by 2x.
Companies often have the high-quality security scanning and detection signal for application security issues only once the app is running in production, but increasingly need to understand issues when the code is written so that they can have a scalable pipeline for identifying and preventing attacks early before they get into production and also when it is less expensive to fix them in terms of overall efforts and cost. Attacks like Solarigate (Zod) demonstrate how security hardening later in supply chain is shifting attacks earlier. This trend of moving towards prevention by including security from the early stages of SDLC with a proactive mindset is known as “Shift Left” and securing the development environment with DevSecOps controls. Here I seek to build the right framework to get a much-earlier security scanning and detections built within the CICD pipeline in a scalable way to productize testing, monitoring, and response to support security drift detection.
By integrating security in CICD, one can deliver secure and compliant application changes rapidly while running operations consistently with automation. In order to do this well, the most logical place security can be checked are code reviews. But now the series of questions raised -
How can it be achieved?
How can we make sure every release that goes to production has proper security sign-off?
How can we scan and test every piece of code that is changed from not just DAST or SAST point of view but also including wide custom and flexible security test cases?
Here we will talk about building such a solution and framework to integrate security in CICD and automating the complete process for continuous scanning of different kinds of potential security issues on every code change in Azure Pipeline.
Some of the improvements it brings -
Wide Variety of Security checks — Integration of standard and custom checks
Early Checks — Now security checks are performed as soon as any PR is raised or code is modified
Highly Flexible —The security checks are very modular. We can add more checks as we want and configure them to perform response-based action
Completely Automated — Automation is the key/let the machines do the work
Alerting - Integration of alerts for check success or failure
Reporting - Scan reports are shared across different communication channels
Framework as code - Any company having their CICD over Azure can use this framework by just running in-house built cloud formation template
Vulnerability Management - All the vulnerabilities and findings are logged in a single place - Azure Security Center
The Simple, Yet Lethal, Anatomy of a Software Supply Chain Attack
by: Yehuda Galb
Download Slide |
Watch Video
Security teams nowadays are struggling to contain the risk of software supply chain attacks on their organizations, implementing control of that sort varies from internal controls hardening CI services /hardening developer workstations to demanding compliance to standards from vendors\contactors.
However, one of the places security teams having harder time is in the field of open-source software.
The use of third-party software components is part of the modern software development culture with over 90% of engineering teams worldwide building and shipping software that uses external code. While facilitating extreme agility, it also increases the attack surface of organizations as seen in the spike of recent major incidents .
It’s known in cybersecurity that you must understand the threat you are facing with. In this session, we will do an overview of the software supply chain flow and deep dive into each one’s weak spots.
We will also demonstrate the ease of conducting this sort of attack and our point of view as a defenders.
Uncovering 0-days in Healthcare Management Applications
by: Aden Yap Chuen Zhen, Sheikh Rizan
and Muhammad Ali Akbar
Download Slide |
Watch Video
OpenEMR is the most popular open-source medical practice management, electronic medical records, prescription writing and medical billing application used by Healthcare Professionals. Security researchers from Project Insecurity and SonarSource had reported numerous vulnerabilities in OpenEMR application prior to 2021.
However, BAE Systems Vulnerability Research team took up the challenge to uncover more vulnerabilities in the same application. To our surprise, we still found a huge number of high impact vulnerabilities inside the application recently. These vulnerabilities could potentially expose medical records and other sensitive patient data, to tampering of the billing information and administrator functionalities by unauthorized personnel. The security flaws were discovered by combining both manual source code analysis and white box testing.
In this talk we will share our experiences of uncovering over 60 vulnerabilities resulting in 8 public CVEs. We will share the key findings (subject to pending patch rollout) and challenges in hunting for OpenEMR VDP. It is our hope that this talk will enable other researchers to get involved in Vulnerability Research and help make the Internet a safer place.
Understanding and Re-creating Process Injection Techniques through Nimjector
by: Ariz Soriano / ar33zy
Download Slide |
Watch Video
Process injection is one of the prominent techniques used by threat actors to execute malicious code and gain access inside the target’s system. It mostly aids in stealth and evasion to avoid common security defenses such as endpoint detection & response (EDRs) and antivirus (AV) softwares.
From a red teamer's perspective, being knowledgeable with different process injection techniques can be handy when crafting payloads that evade such defenses. On the other hand, blue teamers would understand better how a payload interacts and establishes a foothold inside a compromised machine. When either teams are unacquainted with this technique, they could have a hard time producing a working payload or improving the defenses of an organization by detecting indicators of compromise (IOCs).
Nimjector is a payload creation framework written in Nim which enables Penetration Testers and Red Team Operators to easily re-create or simulate process injection techniques based on a template. This tool also allows Security Operations Center (SOC) Analysts or Incident Responders (IRs) to understand and learn how different process injection techniques run and execute.
Inspired by existing repositories crafted with Nim such as OffensiveNim, Nimcrypt2, and NimHollow, this new tool was created to help both teams understand and learn more about Process Injection. It aims to open a collaboration between template creation from malware samples used by threat actors and using these to feed or tune security tools as well to detect such a technique.
Wild IoT Tales: from power grids to oil pipelines
by: Barak Sternberg
Download Slide |
Watch Video
In this talk, we will analyze 3 of the wildest IoT attack stories happened last year - who was targeted? What Malware was used? What was the impact?
First, We will dive & explore the recent attack over Ukranian power grids and show how it (almost) caused blackout for over 2 million people in Ukraine!
We will further technically analyze "Industroyer2", the unique malware used in this attack, its unique ways of operation & cool techniques.
Afterwards, We will describe the Conti-ransomware attack over Public Health Systems in Ireland (HSE) & see for how long attackers stayed hidden in their IT networks!
Finally, we will shortly describe the Colonial Oil Pipelines Attack in US, the damage was done & how the FBI got involved in all that!?
we will explore some of the unique technical techniques, attack vectors and lateral movement involved! This systematic review conclude the wild IoT attacks of the year, and will be based on multiple both-technical & public-reports!
Speakers
Aaron Aubrey Ng serves as Strategic Threat Advisor at Crowdstrike. He is responsible for CrowdStrike’s Threat Intelligence business across Asia-Pacific and the Middle East & North Africa regions. Aaron focuses on helping customers operationalise and integrate threat intelligence within their organisation's cybersecurity strategy. Additionally, he represents the Crowdstrike Intelligence ecosystem and frequently speaks at Security Conferences, sharing insights into the latest threat trends and developments.
Aaron got his start in Security and Threat Intelligence in the Singapore Armed Forces as a Military Intelligence Officer. He concluded 12 years of Active Duty in 2019 and has served in multiple Command Appointments in classified Intelligence Units, and garnered staff experience in the areas of Strategic Planning and Policy Development. In his penultimate tour of duty, Aaron was instrumental in establishing the Defence Cyber Organisation (DCO), which is akin to Singapore’s Cyber Command.
ROOTCON 17 Archives
January 1, 0001
ROOTCON 17
Theme: (Surveillance, Technology and Privacy)
September 27, 28, 29, 2023
Taal Vista Hotel, Tagaytay City
Presentation Decks
Main Tracks Presentation Decks (TAR)
Village Tracks Presentation Decks (TAR)
Main Tracks Videos (YouTube RC17 Main Tracks)
Village Tracks Videos (YouTube RC17 Village Tracks)
RC17 Speakers Profile (PDF)
ROOTCON 18 Archives
January 1, 0001
ROOTCON 18
Theme: Interconnected Realities
September 25, 26, 27, 2024
Taal Vista Hotel, Tagaytay City
Presentation Decks
Main Tracks Presentation Decks (TAR)
Village Tracks Presentation Decks (TAR)
Main Tracks Videos (YouTube RC18 Main Tracks)
Village Tracks Videos (YouTube RC18 Village Tracks)
RC18 Speakers Profile (PDF)
ROOTCON 19 Archives
January 1, 0001
ROOTCON 19
(Augmented Threats)
September 24, 25 & 26, 2025
Royce Hotel & Casino, Clark, Pampanga
Presentation Decks
Official Tracks Presentation Decks
TRACK 01 - (TAR)
TRACK 04 - (TAR)
Village Tracks Presentation Decks (Check back later)
ROOTCON 19 YouTube Playlist (YouTube)
Speaker ProfilesRC19 Speakers Profile (PDF)
Contest WinnersCapture The Flag: Viettel CyberSecurity
WiFinders (New): Shinigami.ph War Drivers
Hacker Karaoke (New): Chrysvel Chiong
Hacker Jeopardy: Balls Deep
ROOTCON 2 Archives
January 1, 0001
Penetration Testing - A Structured Approach by: TheStare
(PDF)
Provide a meaningful perspective regarding penetration testing service.
The Waledac Botnet by: Bandit
(PDF)
Before its eventual take down the Waledac botnet consisted of an estimated 70,000-90,000
computers infected with the "Waledac" computer worm. The botnet itself was capable of sending about 1.5 billion spam messages a day, or about 1% of the total global spam volume.
Unconventional Privilige Escalation by: Tikbalang
(PDF)
Traditional ways are scanning targets for information, finding vulnerability and exploits available. At times MITM attacks, rootkits, keyloggers and the old school Back Orifice are used to elevate privilege.
ROOTCON 3 Archives
January 1, 0001
Øwning the K00bface Botnet: by Bandit and Team
(PDF)
Koobface spreads through social networking sites, most prevalently through Facebook. Generally, Koobface relies on social engineering in order to spread.
The Koobface message is designed to trick recipients into clicking through to a fraudulent website and either (a)
enter their Facebook (or other social networking) credentials or to accept the installation of malware disguised as a video codec or Flash update.
.
Hashes N Hi-Res by: wewitsky
(PDF)
Unleashing the GPU beasts via CUDA.
LockPicking: Fingering Locks for Fun by: JollyMongrel (arf arf )
(PDF)
- This presentation is intended to educate and describe the inner workings of common lock mechanisms, methods useful to manipulate locks owned by or under full
control of the person taking part of this con, and means to protect themselves from intruders possessing bypass techniques contained herein.
The presenter/author makes no claims as to the accuracy of the following information, nor endorses or encourages activities of malevolent intent.
Trusting OpenDNS by: Tikbalang
(PDF)
The Basics of OpenDNS, Pros and Cons.
Wireless Security on the Philippine Setting by: encrypted, aphro and wewitsky
(PDF)
The algorithm WEP uses requires complete synchronization, but data loss is expected in wireless, making it difficult to keep both ends in sync.
ROOTCON 4 Archives
January 1, 0001
ROOTCON 101: by semprix and encrypted
(PDF)
Get to know what the folks at ROOTCON has been upto, the mission, the basics and all that cool stuffs.
Your Tweet is my command by: Bandit
(PDF)
Twitter as Botnet C&C.
Øwning your InfoSec Career by: Tikbalang
(PDF)
Who I want to be? The Good The Bad and the Ugly. To be or not to b. Deciding your InfoSec career path.
Hacking and the Philippine E-Commerce Act by: Atty. Al Vitangcol
(PDF)
Know the laws before breaking something, discussing E-Commerce Act of the Philippines.
PGP Key Signing Party
Introduction by: r4kista
(PDF)
There are two kinds of cryptography in this world:
cryptography that will stop your kid sister from reading your files, and cryptography that will stop major governments from reading your files.
ROOTCON 5 Archives
January 1, 0001
ROOTCON 101:
by semprix and encrypted
(PPTX)
Get to know what the folks at ROOTCON has been upto, the mission, the basics and all that cool stuffs.
Keynote: IPv6 Security Foiling The Hackers
by: Lawrence Hughes of InfoWeapons
(PPT)
Security offered on IPv6 How to Foil Hackers
Console (In)Security: The Oncoming Storm
by: Chris "@PaperGhost" Boyd
(PPTX)
Increasingly, videogame consoles (and their creators) are becoming a primary target for individuals taking part in everything.
Zeus: The God of All... Cyber-Theft by: Roland Dela Paz and Jasper Manuel
(PPT)
When Zeus entered the threat arena, it quickly became eminent and has been the crimeware of choice for a wide range of cybercriminals.
Reversing Android Application
by: Jonell "Jonez" Baltazar
(PDF)
With the introduction of Google Android driven smartphones, a lot of Android App markets
emerged offering free and commercial applications where Google Android Market is
unavailable..
Cyber Terrorism: Is the Philippines Ready For It? (Pending Presentation Upload)
by: Atty. Al Vitangcol
Osama Bin Laden is dead. However, terrorism is still alive and kicking.
As older groups are defeated or exhausted, more radical and more violent successors often take their place.
Terrorism continually reinvents itself in new and more dangerous forms – including cyber terrorism.
Cyberwarfare and National Security in the Age of #Anti-Sec by: Sven Herpig
(PPTX)
Knowing CyberWarFare and National Security in the age of AntiSec.
Introducing TDL4, a Sophisticated Fraudster's Rootkit
by: Berman Enconado
(PPT)
Stealth—such is the nature of rootkits: those nifty little software that quietly slips inside systems without anyone noticing.
They're dubbed as one of the most—if not the most—difficult pieces of programming ingenuity to be seen lurking on technologies that even the most powerful detection applications rarely spot.
Lock Exploitation Techniques
by: Jolly Mongrel
(PDF)
This presentation is intended to educate and
describe the inner workings of common lock mechanisms, methods useful to
manipulate locks owned by or under full control of the person taking part of
this con, and means to protect themselves from intruders possessing bypass
techniques contained herein.
Sp0tting Web Vulnerability
by: SunGazer
(PPTX)
Spotting Web Vulnerabilities and few other stuffs ^_^.
Penetration Testing Web Application
by: Whizkah
(PDF)
Pentesters use different approaches in pentesting web applications, some rely heavily on automated scanners, others on checklists and a few more on combined automated and manual testing.
This presentation will present an approach on how to conduct web application penetration tests that allows the tester to align the tests and results to the clients goals and expectations.
Evilution Of Telephony
by: PCr4ck
(PPTX)
On these presentation it will give you a basic VoIP security, Evilution that emerge on the telephony.
ROOTCON 6 Archives
January 1, 0001
AdverGaming The System:
by Chris "PaperGhost" Boyd
(PDF)
In game advertising is becoming more visible (and in some cases, more intrusive) in the world of console, PC and mobile gaming. In many cases, disclosure related to what's happening with your PII is as bad (if not worse) than the poor practices of the Adware industry prior to clean ups brought about by the FTC and the NYAG.
Where is your data going? What are you consenting to when installing that "free" app? Which advertising networks are serving you "relevant" targeted advertising while playing the latest FPS?
From the first in game ad from 1978 to the present day where as many as 40+ EULAs compete for your attention while installing a "free" game, this presentation will look at the history, development and current state of in game advertising and how it affects you.
A Brief View In Prioritizing Website Security + Demo:
by N1tr0b
(PDF)
The talk is about the importance of prioritizing website security in different points of views. It provides "you" the audience enough information about the damages of exploitation of a website and how to put an end to it. Also a short security code work for the following attacks:
XSS ( Cross Site Scripting )
LFI / RFI ( Local File Inclusion / Remote File Inclusion )
SQLi (SQL Injection)
CSRF ( Cross Site Request Forgery)
RCE ( Remote Code Exploitation )
Keynote ++ Cyber Espionage - How to sell a country:
by Morris Fedeli
(PDF)
Morris Fedeli is a former ACS vice chair and PCS committee co-chair, holding diplomatic status, and a
former ASIO recruit working with NBI operatives and Interpol on exposing Cybercrime activities
within South East Asia.
A pioneer of public wireless in the Philippines and real time collaborative platforms, he possess
degrees in Computer Engineering, Science and Masters in Business/Technology and is the
CEO/Director of a number of companies with business interest in China, HK, Australia, Italy and
Philippines since 2002.
A humanist, he is an expert witness, magistrate, consultant/advisor and former International cyber
bank director who travels up to 30 countries a year sharing his wisdom with others.
With a background in the legal field, he is here today to provide us a business perspective to Cyber
Espionage and How to Sell a Country!
Espionage in Cybertopia: A Government's Tale:
by Sven "zedian" Herpig
(PDF)
Where once upon a time our coporate assets would be guarded by kevlar embodied and armed security guards, today our vaults are filled with the confidential information about our patents and designs, our secret recipes and technical knowhow as well as personal information about you - our client - what are your likes and dislikes, your favourite foods, movies and amusements, shopping habits, reading materials and recreational habits, right down to your secret desires!
Crypto and PKI - Weapons For Mass Liberation:
by Lawrence Hughes
(ZIP)
Crypto is your FRIEND. With even a low end PC you can do crypto that is provably impossible for even NSA to crack, IF you know what you're doing. One of the fundamental tools for living in cyberspace. Like the Colt .45, crypto is a great EQUALIZER. The combination of crypto, PCs and the Internet is one of the things the statists fear the most, and with good reason. Between you and me, the end-to-end nature of IPv6 will make it essentially impossible for the government to monitor or control the flow of information - combined with crypto that's a Weapon of Mass Liberation. A tool that should be in everyone's personal arsenal.
Understanding Sandboxes:
by Paul Sabanal
(PDF)
In the last couple of years we have seen how the introduction of sandboxing into some of most used software in the world has changed the software exploitation landscape. Since the release of Adobe Reader X, for example, there has been no publicly released exploit for it. However, most of us are not familiar with how these sandboxes work. Knowing how they work makes us understand their limitations, and makes us aware of what they can and they can't do to protect us.
Mac Binary Analysis: A Sn3ak Peak:
by Christopher Daniel So
(PDF)
With the increasing popularity of Mac OS X comes the increase in number of the malware that target the platform. Thus, it is imperative for reverse engineers to have basic knowledge in code analysis for this new platform. In this presentation, techniques of code analysis of Mac binaries for reverse engineers and additional background information will be presented.
Malware 101:
by Berman Enconado & Reginald Wong
(PDF)
We already know the impact of malwares in server systems. Understanding what malwares are in the general scope is not enough. We need to know how it looks like and what it really does. This paper aims to give an in-depth analytic perspective on different types of malwares. Most of the discussions here will identify malicious codes and show what those codes do.
SOUL System:
by Joshua Lat
(PDF)
The SOUL System is a secure online authentication system which involves a two-factor authentication scheme using a password and an ordinary hardware device as a security to- ken. The three main parts of the system are the website, the ordinary hardware device, and trusted third party. The website must first be integrated with the web API provided and then registered to the trusted third party website to allow two-factor authentication. The security token is any ordinary hardware digital container that contains ordinary files such as BMP and PNG files where the user's data are hidden. Examples of possible containers include a USB flash drive, a laptop, a cellular phone, and even a Dropbox folder. It must be registered to the trusted third party so that it can be used to register and login to SOUL System integrated websites. The trusted third party stores and provides the public keys of both the two-factor login enabled websites and the registered security tokens.
Surviving ROOTCON (ROOTCON 101):
by Encrypted84
(PDF)
The presentation will deal on how to survive at ROOTCON as CON-Goers. How ROOTCON was planned, how to contribute, how to be ub3rAw4s()me during the CON.
Encrypted with the Goons participation will also be discussing the on the day mechanics of the activities, such as Hackista Challenge, WiFi Warrior etc...etc....
Taking Down a Botnet - The Story Behind Rove Digital's Takedown:
by Ryan Flores
(PDF)
Last November 2011, the FBI has publicly announced the takedown and arrest of a cybercrime gang operating in Estonia. This presentation gives details on how Trend Micro was able to help the FBI in the take down and arrest, while also giving insight on the time span, scale and complexity of an operation of this nature.
Virtualization, A New Risk:
by Tikbalang
(PDF)
Virtualization may very well be one of those revolutionary paradigms that could fundamentally change the way we think about and approach computing. Benefits:
Vulnerability assessment of commonly available personal safety boxes in the Philippines:
by Jolly Mongrel
(PDF)
Personal safety boxes usually contains sensitive information such as, but not limited to; personal details in government registry forms, bank details, personal letters, memos, diaries, company documents and a lot more. The problem with these boxes stems from fundamental errors that could have been remedied at design conceptualization level. Moreover, lack of quality testing (adversarial pen-testing) and skewed functional priorities resulted in some boxes that could be opened surreptitiously; hence, compromise of its contents and further privilege escalation is possible beyond awareness. This presentation is done for research and consumer awareness purposes only.
ROOTCON 7 Archives
January 1, 0001
CyberCrime Act of 2012: Issues and Concerns by: Atty. Al Vitangcol III, C|HFI, C|EI
(PPSX)
The revolution in information technologies has changed society fundamentally. It has given rise to unprecedented economic and social changes. With it comes the emergence of new types of crimes.
These new types of crimes, based on new technologies, challenge existing legal concepts. The Convention on Cybercrime of the Council of Europe, known as the Budapest Convention, is the only binding international instrument on the issue of cybercrimes. Its main objective is to pursue a common criminal policy aimed at the protection of society against cybercrime, especially by adopting appropriate legislation and fostering international cooperation. It is a guideline for any country developing comprehensive national legislation against Cybercrime.
Republic Act No. 10175, known as the "Cybercrime Prevention Act of 2012", was signed into law by the President on September 12, 2012. It took effect on October 3, 2012.
The presentation will focus on the provisions of the law and its compliance vis-a-vis the requirements of the Budapest Convention. It will discuss the various offenses punishable under the law. More so, the presentation will likewise touch on the aftermath of the enactment of the law, including various pros and cons on its implementation. Finally, the law's current status shall be presented and suggestions on the way forward shall be made.
Diving to Recon-NG by: Primarch Victus
(PDF)
Recon-ng is a Web Reconnaissance framework written in Python which focuses on Reconnaissance,
Discovery, and Reporting which are steps 1, 2 and 4 of the Web Application Penetration Testing Methodology.
It is also a Metasploit like framework and that there are separate module branches within the module tree for each
methodology step. In this topic we will cover the Recon-ng introduction, framework information and basic usage.
Getting to know SmartTV by: Joey Costoya
(PDF)
Smart TVs are the next evolutionary step of our beloved household appliance,
transforming this living room mainstay into yet another Internet-connected computer, albeit with a much better screen.
This transformation exposes to the TV to the same attack vectors that has plagued personal computers for years.
This presentation will give an overview of the Smart TV technology and its corresponding ecosystems.
It will also explore what's under the hood of a popular Smart TV brand, exposing some possible attack entry points.
JAVAlicious: Malicious Java in the wild by: Maersk Chastine Menrige
(PDF)
Java is recognized to be the most popular programming language in the world.
It is a portable object-oriented programming language that could be used in any platform.
Its syntax is easy and similar to the C programming language. The Java virtual machine (JVM),
its code-executing component, enables it to run on any platform. However, JVM is a prime target
for cybercriminals because if its flaws. In Q1 2013, several Java vulnerabilities have been disclosed,
some of took a while to be patched. Java vulnerabilities are known entry points used by exploit kits,
which run on Windows machines. Other malware that used Java vulnerabilities also run on platforms,
such as the Flashback malware that spread on Mac operating systems.
In this presentation, we explore the Java programming language and its environment.
In our exploration, we review the Java programs used by cybercriminals, and how these programs are
used in exploiting the early vulnerabilities in Microsoft Virtual Machine's Java bytecode verifier.
We also review the latest methods used in exploiting Java. The review and discussion includes a list of
exploit packs known to use Java vulnerabilities in spreading malware. In addition, we demonstrate how to analyze a
malicious Java applet from one exploit kit to show its capabilities. To conclude the presentation, we provide
recommendations to prevent infections from Java malware.
Mobile Malware Evolution by: Jesmond Chang
(PDF)
It was in June 2004 when Kaspersky Lab first got hold of a sample virus designed for mobile phones.
A few years later and we've witnessed how the number of mobile threats exploded specifically targeting Android OS notably in the year 2012. It was also within that year when the most scandalous mobile espionage events transpired such as the detection of a mobile version of the spyware module FinSpy, developed by the British firm Gamma International as well as the disclosure of technical details of cyber intelligence operations dubbed Red October.
The latest development in mobile malware evolution is happening today where mobile threats have already gone international. What's next?
My Experiments with truth: a different route to bug hunting by: Devesh Bhatt
(PDF)
The Best way to improve the security of your systems is to hire hackers. Unfortunately, companies can't
hire all best hackers, so the companies has chosen another best way to improve their system
security, "Bug Bounty Program”
Google, Facebook, Mozilla, PayPal, Etsy and many other companies pay a good amount to hackers for
responsible disclosure and recently it is being started as a service in the form of “bugcrowd”
Security Researchers have submitted bugs ranging from configuration issues to SQL injections.
This topic is not about what is a “Bug Bounty” program, who all is paying what amount and the scope of
testing. This paper is basically focused on the approach to finding simple and yet devastating
vulnerabilities, earn hefty amounts and share space with the top researchers from around the globe.
Ouroboros by: Chris Boyd & Jovi Umawing
(PDF)
Preemptive strikes against attackers. Mobile Malware on the rise. Government spyware. Printer shenanigans. Cybersecurity lobbying. It sounds like a round-up of the top news stories of the last couple of months - in reality, it's a sample of news stories from 2005 to 2008, when Antispyware companies and security forums clashed over legal battles, death threats, pr spin, Botnet monetisation and more at the height of the old Adware industry's power and ambition.
Was so much time spent firefighting the Adware industry that many of our current security concerns were allowed to develop and grow largely unaddressed? What factors could have encouraged this security groundhog day? Why did the Adware industry's passing encourage a form of "security fatigue" on Infosec blogs? Why did so many security researchers burn out? What might have happened if the old guard of Adware vendors hadn't gone bust or been sued into oblivion? What legacy have the ghosts of those long dead and acquired technologies left behind?
Package Tampering: Injecting jack in the box. by: Jolly Mongrel
(PDF)
Often overlooked for being too common (ubiquitous), boring and dispensable (unsexy), little have we thought that product packages are potential vectors of attack. For a progressive security mind, it can be considered as one of the weakest links in the product supply chain.
Examples of targets are (but, of course, not limited to) personal letters and/or memos, communication equipment, and computer software and/or hardware among others. In bypassing the packages, access to the aforementioned items can lead to gathering of vital information or “trojaning” the software and installation of alien hardware components or replacement thereof in the communication and computer equipment to conduct snooping, remote admin, or other parasitic activities.
This topic aims;
1.) to introduce a new subject on physical security for RootCon
2.) to provide a general view on tampering, giving special attention to package tampering for this presentation
3.) to set the stage for more tampering topics in the future.
Social Network Analysis as Internet Security Tool by: Wilson Chua
(PDF)
Security devices (firewalls, IDS, IPS) produces a huge amount of data by posting each security incident/event into a Syslog database. This (big) data enables the system administrators to identify the source of the largest attacks, and the most frequently victimized/targeted server.
However, due to massive number of records generated by Syslogs, a quicker and more timely analysis is needed. Social Network analysis is presented here as an optimal way to quickly analyze and create actionable insights from this huge amount of data - by converting (big) data into graphics format.
Stealth by Legitimacy by: Jeffrey Bernardino
(PDF)
Nowadays, its commonplace for cybercriminals to create complicated malware. But as part and parcel of any trade, cybercriminals update themselves by continuously uncovering new techniques to improve malware stealth. Misuse of legitimate services is one of probably hundreds of ways to cover cybercrime tracks. Trend Micro has discovered this with BKDR_VERNOT malware. In this presentation, Trend Micro discusses malicious routines of a particular BKDR_VERNOT malware. We also dive deep into the advantages and disadvantages of using legitimate services by malware - how BKDR_VERNOT used legitimate Evernote C&C, and how this technique will influence future attacks.
The VOHO Campaign - an in-depth look by: Christopher Elisan
(PDF)
In July of 2012, we discovered an emerging malicious code and content campaign spreading at a rapid rate within very specific geographic theaters. These clusters were confined to ten geographic areas and involved thousand of hosts. To the untrained eye, this looks like a common “drive-by” attack mechanism but additional analysis and research show it to be otherwise. This presentation sheds light in the new attack, which we termed “Watering Hole.” The talk will cover the deployment method used to spread the malware and the malware’s behavior once it reaches the target system.
Unpackers in a World of Signature-less Malware Detection by: Frederic Villa
(PDF)
Malware authors use packers to keep their software undetectable without changing the code. Malware from other families also use these packers to exploit the limitation of AV software until AV companies started creating unpackers.
Unpackers are created in order to expand their detection coverage. Once an unpacker is created, packing the malware seems to have become a futile task.
As the antimalware industry move towards signature-less detection, one may think that packers will cease serving its purpose. In this talk, we'll discuss how unpackers can still play an important role in malware analysis and the various tools that make unpackers easier to use.
ROOTCON 8 Archives
January 1, 0001
ROOTCON 101:
by semprix and encrypted
(PPTX)
Get to know what the folks at ROOTCON has been upto, the mission, the basics and all that cool stuffs.
Keynote: IPv6 Security Foiling The Hackers
by: Lawrence Hughes of InfoWeapons
(PPT)
Security offered on IPv6 How to Foil Hackers
Console (In)Security: The Oncoming Storm
by: Chris "@PaperGhost" Boyd
(PPTX)
Increasingly, videogame consoles (and their creators) are becoming a primary target for individuals taking part in everything.
Zeus: The God of All... Cyber-Theft by: Roland Dela Paz and Jasper Manuel
(PPT)
When Zeus entered the threat arena, it quickly became eminent and has been the crimeware of choice for a wide range of cybercriminals.
Reversing Android Application
by: Jonell "Jonez" Baltazar
(PDF)
With the introduction of Google Android driven smartphones, a lot of Android App markets
emerged offering free and commercial applications where Google Android Market is
unavailable..
Cyber Terrorism: Is the Philippines Ready For It? (Pending Presentation Upload)
by: Atty. Al Vitangcol
Osama Bin Laden is dead. However, terrorism is still alive and kicking.
As older groups are defeated or exhausted, more radical and more violent successors often take their place.
Terrorism continually reinvents itself in new and more dangerous forms – including cyber terrorism.
Cyberwarfare and National Security in the Age of #Anti-Sec by: Sven Herpig
(PPTX)
Knowing CyberWarFare and National Security in the age of AntiSec.
Introducing TDL4, a Sophisticated Fraudster's Rootkit
by: Berman Enconado
(PPT)
Stealth—such is the nature of rootkits: those nifty little software that quietly slips inside systems without anyone noticing.
They're dubbed as one of the most—if not the most—difficult pieces of programming ingenuity to be seen lurking on technologies that even the most powerful detection applications rarely spot.
Lock Exploitation Techniques
by: Jolly Mongrel
(PDF)
This presentation is intended to educate and
describe the inner workings of common lock mechanisms, methods useful to
manipulate locks owned by or under full control of the person taking part of
this con, and means to protect themselves from intruders possessing bypass
techniques contained herein.
Sp0tting Web Vulnerability
by: SunGazer
(PPTX)
Spotting Web Vulnerabilities and few other stuffs ^_^.
Penetration Testing Web Application
by: Whizkah
(PDF)
Pentesters use different approaches in pentesting web applications, some rely heavily on automated scanners, others on checklists and a few more on combined automated and manual testing.
This presentation will present an approach on how to conduct web application penetration tests that allows the tester to align the tests and results to the clients goals and expectations.
Evilution Of Telephony
by: PCr4ck
(PPTX)
On these presentation it will give you a basic VoIP security, Evilution that emerge on the telephony.
ROOTCON 9 Archives
January 1, 0001
How to Shot Web: Better Web Hacking in 2015
by: Jason Haddix
(PDF)
2014 was a year of unprecedented participation in crowdsourced and
static bug bounty programs, and 2015 looks like a trendmaker. Join
Jason as he explores successful tactics and tools used by himself
and the best bug hunters. Practical methodologies, tools, and tips
make you better at hacking websites and mobile apps to claim those
bounties. Convert edge-case vulnerabilities to practical pwnage
even on presumably heavily tested sites. These are tips and tricks
that every tester can take home and use. Jason will focus on
philosophy, discovery, mapping, tactical fuzzing (XSS, SQLi, LFI,
++), CSRF, web services, and mobile vulnerabilities. In many
cases we will explore these attacks down to the parameter, teaching
the tester common places to look when searching for certain bugs.
In addition he will cover common evasions to filters and as many
time saving techniques he can fit in.
ROOTCON®20
January 1, 0001
Safety Waiver
January 1, 0001
Agreement and Release of Liability
By participating in ROOTCON Events, you acknowledge and agree to the following terms and conditions. Please read this waiver carefully.
1. Assumption of Risk
I, the undersigned, understand that participating in ROOTCON Events, including but not limited to workshops, villages, contests, and other activities, involves certain risks, hazards, and potential for personal injury or property damage. I willingly assume all risks associated with my participation in the Event, whether foreseen or unforeseen.
2. Release of Liability
In consideration of my participation in ROOTCON Events, I hereby release, waive, and discharge ROOTCON, its organizers, sponsors, volunteers, vendors, and venue from any and all liability, claims, demands, or causes of action that may arise from my participation in the Event, including but not limited to injury, illness, or damage to personal property, whether caused by negligence or otherwise.
3. Medical Treatment
In the event of injury or illness, I authorize ROOTCON staff, volunteers, or medical personnel to administer necessary medical treatment or assistance. I agree to assume all costs of medical care, and I release ROOTCON from any liability resulting from such treatment.
4. Code of Conduct
I agree to abide by the ROOTCON Code of Conduct and understand that violation of the rules may result in my removal from the Event without refund. I acknowledge that the safety and security of all participants are paramount and agree to behave in a responsible and respectful manner at all times.
5. Photographic Release
I understand that ROOTCON may record or photograph the event and its participants for promotional purposes. By participating in ROOTCON Events, I consent to being photographed or filmed and authorize ROOTCON to use such recordings for future promotion, marketing, or documentation without compensation.
6. Indemnification
I agree to indemnify and hold harmless ROOTCON, its staff, sponsors, volunteers, and venue against any claims, damages, losses, or expenses (including legal fees) arising from my actions, negligence, or violations of this waiver during the Event.
7. Governing Law
This waiver and any disputes arising from my participation in ROOTCON shall be governed by the laws of the Philippines.
Updated: Sat May 30 20:28:20 PST 2026
Revisions: 59397869d4f5174764d5dcc409082cdfc92f7480
Sponsors
January 1, 0001

Established in 2015, Pentera is the market leader in Automated Security Validation, empowering companies to proactively test all their cybersecurity controls against the latest cyberattacks. Pentera identifies true risk across the entire attack surface, guiding remediation to effectively reduce exposure. The company's security validation capabilities are essential for Continuous Threat Exposure Management (CTEM) operations. Thousands of security professionals around the world trust Pentera to close security gaps before threat actors can exploit them.
www.pentera.io
Terms and Conditions
January 1, 0001
Readme
TERMS AND CONDITIONS
1. Introduction
These Website Standard Terms and Conditions written on this webpage shall manage your use of this website. These Terms will be applied fully and affect to your use of this Website. By using this Website, you agreed to accept all terms and conditions written in here. You must not use this Website if you disagree with any of these Website Standard Terms and Conditions.
Minors or people below 18 years old needs to have adult supervision when visting the site.
2. Intellectual Property Rights
Other than the content you own, under these Terms, ROOTCON and/or its licensors own all the intellectual property rights and materials contained in this Website.
You are granted limited license only for purposes of viewing the material contained on this Website.
3. Restrictions
You are specifically restricted from all of the following:
- publishing any Website material in any other media;
- publicly performing and/or showing any Website material;
- using this Website in any way that is or may be damaging to this Website;
- using this Website in any way that impacts user access to this Website;
- using this Website contrary to applicable laws and regulations, or in any way may cause harm to the Website, or to any person or business entity;
- engaging in any data mining, data harvesting, data extracting or any other similar activity in relation to this Website;
- using this Website to engage in any advertising or marketing.
Certain areas of this Website are restricted from being access by you and ROOTCON may further restrict access by you to any areas of this Website, at any time, in absolute discretion. Any user ID and password you may have for this Website are confidential and you must maintain confidentiality as well.
4. Content
In these Website Standard Terms and Conditions, “Your Content” shall mean any audio, video text, images or other material you choose to display on this Website. By displaying Your Content, you grant ROOTCON a non-exclusive, worldwide irrevocable, sub licensable license to use, reproduce, adapt, publish, translate and distribute it in any and all media.
Your Content must be your own and must not be invading any third-party’s rights. ROOTCON reserves the right to remove any of Your Content from this Website at any time without notice.
5. No warranties
This Website is provided “as is,” with all faults, and ROOTCON express no representations or warranties, of any kind related to this Website or the materials contained on this Website. Also, nothing contained on this Website shall be interpreted as advising you.
6. Limitation of liability
In no event shall ROOTCON, nor any of its officers, directors and employees, shall be held liable for anything arising out of or in any way connected with your use of this Website whether such liability is under contract. ROOTCON, including its officers, directors and employees shall not be held liable for any indirect, consequential or special liability arising out of or in any way related to your use of this Website.
7. Indemnification
You hereby indemnify to the fullest extent ROOTCON from and against any and/or all liabilities, costs, demands, causes of action, damages and expenses arising in any way related to your breach of any of the provisions of these Terms.
8. Severability
If any provision of these Terms is found to be invalid under any applicable law, such provisions shall be deleted without affecting the remaining provisions herein.
9. Variation of Terms
ROOTCON is permitted to revise these Terms at any time as it sees fit, and by using this Website you are expected to review these Terms on a regular basis.
10. Assignment
The ROOTCON is allowed to assign, transfer, and subcontract its rights and/or obligations under these Terms without any notification. However, you are not allowed to assign, transfer, or subcontract any of your rights and/or obligations under these Terms.
11. Entire Agreement
These Terms constitute the entire agreement between ROOTCON and you in relation to your use of this Website, and supersede all prior agreements and understandings.
12. Governing Law & Jurisdiction
These Terms will be governed by and interpreted in accordance with the laws of the Philippines, and you submit to the non-exclusive jurisdiction of the courts located in Philippines for the resolution of any disputes.
The Fork Meister
January 1, 0001
The Fork Meister
Key Fingerprint: 98A6 CD93 8512 03FA E8D0 9073 2FE2 DF9C 5600 117C
semprix [at] rootcon dot org
  -----BEGIN PGP PUBLIC KEY BLOCK-----
Comment: 98A6 CD93 8512 03FA E8D0  9073 2FE2 DF9C 5600 117C

xsFNBF3dk8YBEAC4q/U8Jl0f4KrJf+CeEUXHpwhXaGBvReksxT5bXEcPTLiegpWj
JQC/8Z8B7C6yjfdN8KI8BVDnpNNNMOZ2Z7P84TrGl9kkKW3pYSW8Cjq6J5EgA+Yr
69wZd6pYuzYB2zJHSH2hVjdr4L9RjawgbBDyO7L55y3FpSeUxO59EEhwyq8eHiUv
hnLOtjQKB3+ODiSotlmmrJRqxFOoF9+7jgasXbiLNRAGAkaOajLhqXJdFvBn9Q0L
y6s7Pb9eJrDOtrnorIk5HzkK/6rAHPjUZ++WR3F8IVXJpIGxWXbGBskkWP1UUmdd
tGBjFz2dcKUC98H7mcPF8Yc+NnpPQs//OGqHT4oRPGTbN+c/a/dvsjBiGw/zOyxF
WqbbQWA9q2H6bEQbqCYLHsV57zzC8ZN8Yj0pSMfvUpM4rZ9wP/65BbadtA4z1mqh
qRAvEcA+N5TgOeFYyyimZaroc2goeoouzRRZBSeKX+TkmxrCiiMHv3Nj8ffk9xu4
gQFc5R0lJ36SXsIs7/Cq/tbZWbEKMMLzAClzsvk3vKdf9xw+HhsYAWSYhDiltAf4
RWhZOYAVgbSKrE4ESiHfNEwQ5/U2J4FZodV105SRsUbeZ2MUROPSXv9+PgHnwObS
eKHw+hawDjdvRK0ZG+eRMnJAQWKkuHDT5WE8d7laX8uhvqdsI16YKtnR5QARAQAB
zR5EYXggTGFicmFkb3IgPGRheEByb290Y29uLm9yZz7CwYsEEwEKADUCGwMDCwkH
AxUKCAIeAQIXgAMWAgEWIQSYps2ThRID+ujQkHMv4t+cVgARfAUCZv+YVQIZAQAK
CRAv4t+cVgARfMLKD/4oT6sn187AiL1OGxyyMVUHVIUQexMSYoW5zEAkfXLZya2e
DGAsctoDamTO3oVfiqxT3T+g3w0fJ0mjtASOlZeZV/IpNTNkFUM1W5a+H41eCNeH
iBJPMjNAmrjDxTKahUSkpvjyY7LX47ColzsonXS8L4iM6r22EjTbfOKISzfPSsir
pyY+f+VbPUc2sEoRyVYHAitKbDhd5mOO2swAy7ABEiJmHJZkBEYqwVx+Ws92+HgL
T8+lqYiC7LlX0RcXF1LSo102OP6Jvp3g3hnds0Ig0rt+pLS6pcOwmvO+1czZc698
bdWWWpV752EqIBmktQ5BMa3jmqr3Om9m6Ao6nZz3V3q1IoWNM7MSxDsbP7AX1hD/
CkZuw0Vsmpq3JZnP0mMGrSIZrUFqiz2GTpN4c9QTCNN1OTbr4QZAHtqZtdsvXNQK
VtuVUFteqYiHofJshKWOl88fMLWSjEvsPit4iaWzR7u42RSNEWNAmXughauKMgkc
5qEoRTOa6a62rp5IL5bckxIvkYGQUXfQSdm/HKCz+pI4Zw5Yd5sh85L6dilpAIHI
wPMlEBhrqZaBlv4/P+oskI9NAVTf2h2LQNwq5t/acJUZpqmjGR26rpoVxCvKzt/G
dfwOybeLDE/U/SO1CaL/AZwGdmcGkYde3pELhP1bifN7YMLCEIxT1U3Hy6cXv8LB
iwQTAQoANQIbAwMLCQcDFQoIAh4BAheAAxYCARYhBJimzZOFEgP66NCQcy/i35xW
ABF8BQJm/5FoAhkBAAoJEC/i35xWABF8tMMQAKyt6/n/OYBg2WDTcKgdOlywc/HI
SlFiwGIBOTa9YOtXQsjNjaeMkaktcU13Vmj/eLM1W+v6Yfk40bV3NwXu9ApfgZY4
2jmYaBWVeEGgJLYRLlWf2iNTR7NJl83MDPCL6c5GQcmKBDcLsq33w773RcKOjSVT
8cff5KJY58br4lgGEEy26HMxxMPLZvdq9go37fozPkffKbd6qlnEXkvVxOGEycfI
YXhoPal+kVEofEcp6ZtWnihmOCQUIXJPe9J/O8GNCJcp4WNi5u8GgfmeBZcBVn8v
XAxVQ3kPl3p3JtYAbILTyy/djt0Dk7CDKFuJlm1T/Xgh6Vzd7fntVL28a7DIli6c
GvtEB1qI+ousviiSXbh7VhAeWbq9Nq62hkd4Wq21VZwTR1uMG061KOYDT4+Js7Lb
W2uhi+RRurf/Fdn7UXUr0BICkJWbNJDaNMYLlsEYXpZQhVz19Qaw9GbKVIt5sefs
r8cEmBP34mEnq+eCZ+klPoRWw0snOUAvgD3Ytrs25eIiTLAWnIceRpoNIGVGsMgM
D0my4FVPFRIR0KXyhgnrRyNc4YxWWskbstr6UEeasSubQNyWCgW6N1PEeYXF5f9E
lfBVHarhGeDKP+MPtk6KqAmKF/StgXX9m0mLirGh0BZnOCEuWNLIOEzwOYSllk7x
Z228g/sL3LoRh+3UwsGIBBMBCgAbBQJd3ZPGAhsDAwsJBwMVCggCHgECF4ADFgIB
ACEJEC/i35xWABF8FiEEmKbNk4USA/ro0JBzL+LfnFYAEXzuXRAAuEgQmycEyk20
hE/cMv9gelcQYNwCzaf46j4Fq7qY5tRniz8fNkkwBF+SfemT/bz6DNLvfDi5IJYg
txt//OIOsPPjaDz8xq5qFv91zX9q9uwxghIPG6bcI1+FrrMXIMdvRDm4lftV6ObJ
iGaUbEAHXg/ODLbGXqVHzMMmE0Rsbr1Y1tQRTGnJin7gISlj0IAudUsCPUAp8zEz
K84MDJhWIoyrOA1s3UxJiu7ev6TkbQeo2uMRZ0rK/CCpd+IGQw/4/+67iJIy+72B
XVPK+vjO56HSd/Rlz1WttpA8ZZknoY1fkRGEWB7KNN4BuJvxJ496JSnG8dj2rlVo
+7A7AQJhP9aTzbeGde0mSFOoWtIs3Xw8+b/y4S8a7oZHPmxv0AH8XCQlSKL1O91f
eKNQnNwWe0IqO69/ahr5Qm5H6raCwxwXLpkykIBm3XuinOOmIZXdrPNC+6JYbsM3
q0NincKoZ25n1kE8W7UFzPfl9C14iLPTYSIFTLkTFDW3GSJ+tjjF4Sd/FpQs/nBt
GA7a6gTJS8syWKUAyaDt/q7OUtKc3WHlZHmGTpipNK3dJXHp0nLlHLKeUlgyFQJB
81ir4Okdclie4vsdxYvekR0TDgT5HmFTZjYLM8hUUIH88XQkD8X0Wygcdc9K0Gv6
MoXB6Q9B+JgQ50YfwkaOU7MZY0DeqaLNIkRheCBMYWJyYWRvciA8c2VtcHJpeEBy
b290Y29uLm9yZz7CwYgEEwEKABsFAl3dk8YCGwMDCwkHAxUKCAIeAQIXgAMWAgEA
IQkQL+LfnFYAEXwWIQSYps2ThRID+ujQkHMv4t+cVgARfEE3D/44htec8Wh+QQZx
954DRF1M4TmurrVTy0EXeOrmJt5BALCTFrSW6dqxbZQNcbgQb6yE5zmnwbaKiTOm
2aVsThFGFPh333P+tiWuYi+z1eczkkn/VJwGwZZEsZUyS7KGTzpLaLomjXG9km/k
hrV+EfMMy+iSvBplqhQjv5EmO05tje0jw1rLQWceP5cGf637hzYf5+8Knb9TkAdA
96LOPTI0cimya8bDdlZWZ9oPL2nxu6YNjLafPji/eafL1IFR2dd1EbmpYlNnUrLC
HMXGXgbPusAswvqx/kFSYvoKcIe0m0xe1jUYRuRrqOtqASTXbsySlCG8KEhfTstq
g/ntj/r8XnwU5SJ8TvFo8w+xulSK1Qn7SKBy5E4J/W+iDi/jW42gW0/bzA/vOoB0
vguNFTnT6NYcGRyw9eDnQgkwQ8CujoMoipUkkcdjkXAQ1A86U2CQv2phS8bZ+8Op
Vg7CzI0bwoBo65AReE4uPUnNsJfX4kCyhWaZom5iUNVGYU4AkVd/O4pE088mSGPf
HzR1rnWMsw3VAMHkgbPmgv1nAnaCGPJVx0hKUD4YOu66X3s2kUBmwrA5BqJfdy/b
zqhJibZXl3R931atmEx343QSxqL+Moua+YFgr0kiFqODPckTNbiinIqAZ3tDEIhG
pYcCahnjjMp5h3i3u74SP9/90QsmLc7ATQRd3ZPGAQgA4Gn9OUpK2XSEsYRgX7hO
BulZ2CbdPjlc7BPub2D069G0DgH8QIAlIoIkXriX50RPeC/jpS3RnmXTsq/GCrqm
g2F7SWa3QUzl3b8JQAuSrVI7QBqiYlF5pSglb3JiL87RaCeGW6UMCdaXQtLA97el
K1++AX+O3vzSrc+94zEmcMmNPRGJe2HRe559uVeqUngi+s6KqvC5TqrY4PjZU6Gk
OiJGmzIIaRC45RU1DoCqXRKjNZSbm1BxKZZXcgsd4pDR6y7b5j79qhQ4730dy6/8
FIKTUsd6iihHK9wk9vOArvtQ5/3Auk9DlPxcT5fvmUePdMiRikYh2TuwuI5e1dC5
GQARAQABwsKVBBgBCgAgAhsMFiEEmKbNk4USA/ro0JBzL+LfnFYAEXwFAmb/mUoB
KQkQL+LfnFYAEXzAXSAEGQEKAAYFAl3dk8YACgkQjUjTuvLXuzZEswgAiqguqrV7
BebJOXaqSIPPvDOwaLDC28isHsMimXLUhf4aJ4kh08tT66plE6SpOaYIHBsnuTmx
bVlSwn2VLv7irEF8PVB5Ri3osGH5Ug5/BRbs3WMx0QxBq9Em1JBRPI/hJwl6DVaS
WCsw30s+Hujcf1e7nBmyKXryS3shuugNhPutL1PunoI6ZbfiP3wIhaFZD7Emg0mS
rugQD5As4OUtOEWdMmtItsHCb3ebb1zfBSqDY2pyH3THVAJ62fD7JyeERQI5Hlk8
6mhfp+y5VZRE1H7CovIjQGAPSFZaNKSGzIJI8tj59hOEH1xvlwtcr1000m7pf8ML
XNKZ1L0JdyidlDA2D/9xGHZmKonli4RqNfiuhfs5RarujDYfz906iPyUFDVWZgbE
xO9ovv0QryuGOHagjNd+mdi73Be50wFk1oPQKWErBTP0D3LjEBRN+KcE7840FukM
+leM/suX2oFRhw47NhL+ro5qTHbdvQvYUFLT2ahICR0VLFL3QKe/Qc/oLm/Ua9W7
3c7JbSxKA46HzGkRLz0dMPb/Is8b23+Cy8wi2mTvmWRLGdtlsgpqYuwsdMVVAnUU
IRJQSzy+/P++0Pfr/wtB3QiEx4Bcpf8UGWjSTvVzZELJMquZI6j8u4D2LYEd3QkS
CKEgByHVBcBVP05wdKQRGdZMwpdK+xZY6g2dagGs/wam6GqaF75nMU/HPImI6NTV
SyaIKBGKbrrViIPdQQ6RjB3kdGv1TxELugwcDej8zqXnXMEBbROkq/9wJIfOfloY
PqnAq23fSy5+geom87Kjz/bThi3s2T3XfCWi6yThFM2P9fSPm/Ytlt5YFYocSHHW
0UsgHhGzAdMDoPnJ5u/GVwWx34UETbTuTKJxZmlCWr+Ym5Iuz4pO5ktu0mSuWAlc
95fDXg+rqR5DZS7eNuyxwHXzMUfzSc7Q3YDSQ6Yo4qu5jht9qNs+EqyqXoNamoNA
j3gotstbjRDmDTSld3D14qi9nweuDDYbaHT3/N1HiC2Tw4mYWDPC1CddWyeIpsLC
mwQYAQoADwUCXd2TxgUJDwmcAAIbDAFACRAv4t+cVgARfMBdIAQZAQoABgUCXd2T
xgAKCRCNSNO68te7NkSzCACKqC6qtXsF5sk5dqpIg8+8M7BosMLbyKwewyKZctSF
/honiSHTy1PrqmUTpKk5pggcGye5ObFtWVLCfZUu/uKsQXw9UHlGLeiwYflSDn8F
FuzdYzHRDEGr0SbUkFE8j+EnCXoNVpJYKzDfSz4e6Nx/V7ucGbIpevJLeyG66A2E
+60vU+6egjplt+I/fAiFoVkPsSaDSZKu6BAPkCzg5S04RZ0ya0i2wcJvd5tvXN8F
KoNjanIfdMdUAnrZ8PsnJ4RFAjkeWTzqaF+n7LlVlETUfsKi8iNAYA9IVlo0pIbM
gkjy2Pn2E4QfXG+XC1yvXTTSbul/wwtc0pnUvQl3KJ2UFiEEmKbNk4USA/ro0JBz
L+LfnFYAEXx0sBAApjR2Tv9e81+pXh9PlfBMmInc3mYP11rJ5b/MR7NhbK6rTDoI
SmqMbjP4A3NVRhb8ZLjwkMEuxzWNeTVFObr6Ph8GMWxq4Iwq8DuKAttmUMcXor92
pVo9OO2yjKId+DPB42kBrrNYJ4HJKuugkrNMUTSxd7JyU29vAdDeW9ZGQAP+P9D8
n1879d0TQBT2WUl+Ssrdm8oUdKU2Lwg2K5AORvMuA6eiRjYvAK1HWfLY6fRanIkF
RHFmJ7E05yClYooIt+4magLqjAFGdFk1jdtEAR5uKrJMlq91KZmEyXUmk+yUv+co
VOV+SiXb8A2d+DVgnC4p82IlBHJGwe2Ubaf/IhtXKzN3ddjJoZ/iyerVpzZ4ZFgI
cY2UiniY9yh7su6m4QykBDYVDtHkTjjsD6dbbwo1fNFNaLgumpZlCPkJQNBM61s1
UFuA8IArNDo4APwc7klOhMjTBxgDG5GjaM9efOHj2IQFG3jy4qsRz12+9DupeT7S
/YvkeJWwlJHYErMzDpRVUKt+Sg5hXSmmgItPW0HxnQm2i6xdgx/kuoTEPv0oE4W4
EqqPu23uONiHaxRIwxehwL1CThbz+gQ9X9wDSxGyHI7Od+R63/ZZVzpVj3ohBVGf
dJmwhA4dM3DEPVCJ0t82Ce81NeO9Z3vp2kh3YItFw3ZFk+vNFG0gbldlt6HOwE0E
Xd2TxgEIAOJsyz3juPpPKVbMHVgUPdf2BddloeHOsApprZk+FB0aZz4KhtBh1+Zm
oQjSdY0awEbeptVw2esAcQcD1t9owlpUCntuyxfkRO4njwxlW6ODY3NWVvS+0n7P
k5AyIqSSk1BnmdUEG3BX9vbzll7v1U3PNv8hHEJs+ZJXLyHvy7xWtlUwNb3OdVUW
CGEaqLI7FYLZagRdUTs6hDYlKd95O+KHAJDEjORsYBQMpN3AHQijiqXp8dMtQt8K
6ExFxm9jxaqRKkLbEJAigCtKlPVPbO9Ksf20n6uZYeFsbhyTT0Qo6SWBndEt64Qx
XKtZCN2sDj1HlG7E1ETWuEN7t+4WaHEAEQEAAcLClQQYAQoAIAIbIhYhBJimzZOF
EgP66NCQcy/i35xWABF8BQJm/5lZASkJEC/i35xWABF8wF0gBBkBCgAGBQJd3ZPG
AAoJEP3+NjFXG3/HS5AH/2sP1mpQSUiLGHOM18LVPP1M41VcxllD6WIesCkjs+yz
ZxVFdGlEezynxG6P/7JLXYZVk46Ms63bg0RbYHR8LHm8nOZ7ZpeaEu0uC0he+EJq
Bdq+LW4Wh0l6Vb8cYp1YzZ5oYMBXWPP1nqQunYxTFSK8TS0/XOi3mreJShBNr3U9
J11bOxXpjnocLazc9zEkU6Pxy9SfG5otBaJQPkE1gNmW+F5rGkk27xltI61g2nkN
EPZQwi17yW+cO+1qrDhUWHqUpqi1ogpZLRo5hAHN7p8bLeLnspBXjGUL69JI7LJF
bQyb9+0HW0pdDFebVpRCGFZBY6w/2pSnwLOI7JvuOUXJmQ/+NKUKclPap5GGX8IG
WpQmDOtZvk4AU4GIMXzHFvCJKLSPk/X4WGDZly2EUZPaO4CcBpoeCWVN8jusnFQ3
DfZRvUHGD3qKrvnfcu+5bLYOsF2rgH8IgPu1dFZ34pJEO4gW07LU+MGNQiOtC8sL
gCAqnTw75XPsFhMRLg1MRH8l9b178gp0LTSBP9ABPoRxW7KOrmKOMmaPGkCtIj8v
yn5B6OCqwVbXSUIUAtgxlsA3GpKpkmMO6DFf9EJVRT6HVOvoRiPlGdWUjS2rNIEZ
mLvmihXSLOvt1T3qIo/V8ZSJ9noU4U3tuIdSqdR1H9JAJZvf/Ay4aZfobsvUiY/H
9Ws1W5zCxqeC5+tsafT0m9c6svATTSJyvYil3AaeHs6A5LtPaunscqXYdR2boWUW
crvnYE0ynTmAkytVVSNeQd1QfDyCgHo2K1yJeLG2h5wagMUkiJ97itrs1hrZ50wn
Z7xkVmh5KgAX8Fb8TojBCbzVM63119GY5dJ7QhIDzOg3izAXx3YqOQ5KKhzWL+8Q
ovcC6e2ZExMxabSOmLyCFal+s3Ngw4sxK7oCZHxIGigv4kv44kbguUYc1vPWinGM
H/yyDSHJdisKuizOQGomn3dG53jPARyjvJdkOJXWXWj4HX1YlwIBigHrlq9RqI1J
gnrR3/tZvtfclJUUzdwUPMek3kDCwpsEGAEKAA8FAl3dk8YFCQ8JnAACGyIBQAkQ
L+LfnFYAEXzAXSAEGQEKAAYFAl3dk8YACgkQ/f42MVcbf8dLkAf/aw/WalBJSIsY
c4zXwtU8/UzjVVzGWUPpYh6wKSOz7LNnFUV0aUR7PKfEbo//sktdhlWTjoyzrduD
RFtgdHwsebyc5ntml5oS7S4LSF74QmoF2r4tbhaHSXpVvxxinVjNnmhgwFdY8/We
pC6djFMVIrxNLT9c6Leat4lKEE2vdT0nXVs7FemOehwtrNz3MSRTo/HL1J8bmi0F
olA+QTWA2Zb4XmsaSTbvGW0jrWDaeQ0Q9lDCLXvJb5w77WqsOFRYepSmqLWiClkt
GjmEAc3unxst4ueykFeMZQvr0kjsskVtDJv37QdbSl0MV5tWlEIYVkFjrD/alKfA
s4jsm+45RRYhBJimzZOFEgP66NCQcy/i35xWABF8migP/2cItxUqSMl5n12dU9mS
dyb5a147skXmiCJOlMbFQaIgFVNy/qIiOeQcd+rlbjrUuqcnuddxScKa1hlD1t+w
Iyb6ftDG41Q4k37EthE6ixdKTqwhMu8YoKL332bp+CmloJCOXtmeGqRkuqdJZZX/
Rh0CR9ig9l76hQNV7FFO5qnvhp02fAoB5ZaRDP6lXI2tmFvY2+RfL/54qh1rxiBI
5c3Hqo796ftIJb/lVTpE+zmShgEDk25kkgNyaNQ+3DVQn6fgyRBQq9NhZ6q06H+G
fHlHoJsHitrW+0/iDULselbTLhZO+aEYUtfoV9RPwXpM2QsAEALPJr5v2Jb/Z6pw
76Z27LsoheYBGya2fHfIC4NIfpiDIxxU+qTpiLtW/CL32A6jGUeZAYxzdv5FKlAy
gfkVYo+7Xo5MF13qV23FHIxppijmQnVPn2T9cjlEZ4VOYo9+AHIO6Wt7ZI+LLozM
2JZmDAI9U945pzIS7X3kp98KPo4zkiP0FeNVty3DCBLBOngdbnr0x8iE+khnqNxW
m9RYgwyKrFDjl28QFfB0SGeG2nD3K17GoS37eKYXLf5HyduMwdkW8vND4zGbFkhf
fIiqV9O0q32dbytDkb7ODzJOKJGcYGeOVG1OCHoZ1T+Zl6uXI+aMh2HdMP+glPSB
NODJQEUgkz/2+kaujvdQT5jb
=dmSC
-----END PGP PUBLIC KEY BLOCK-----